Online technical screening for cyber security roles.
Easily screen your applicants with hands-on technical labs specific to your role. Quickly find your top candidates and supercharge your technical interview process.

Maya Andersen
Candidates
Maya Andersen
94 14m HIRE
Jordan Li
91 19m HIRE
Priya Raman
87 23m HIREThe candidate's screen
Real environments. Real tools. Real work.
Every challenge runs in a live environment built to match the role - a Sentinel workspace, a Linux shell, Windows Event Viewer, a real inbox. This is exactly what your candidates see.
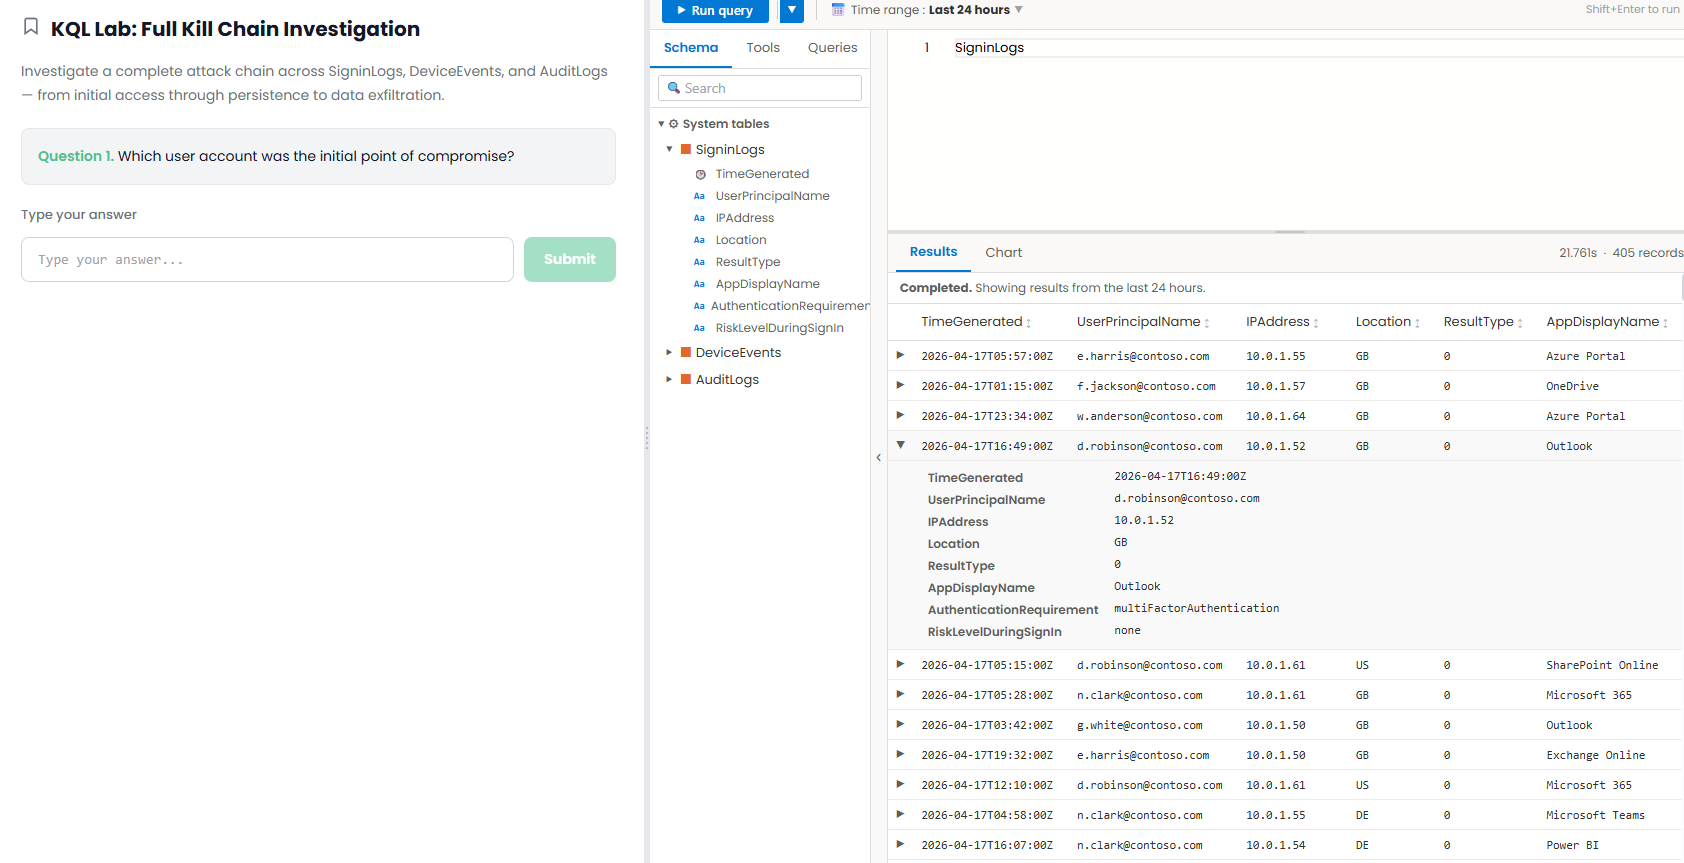
Full kill-chain investigation
Hunt a live attack across SigninLogs, DeviceEvents and AuditLogs - from initial access through persistence to exfiltration.
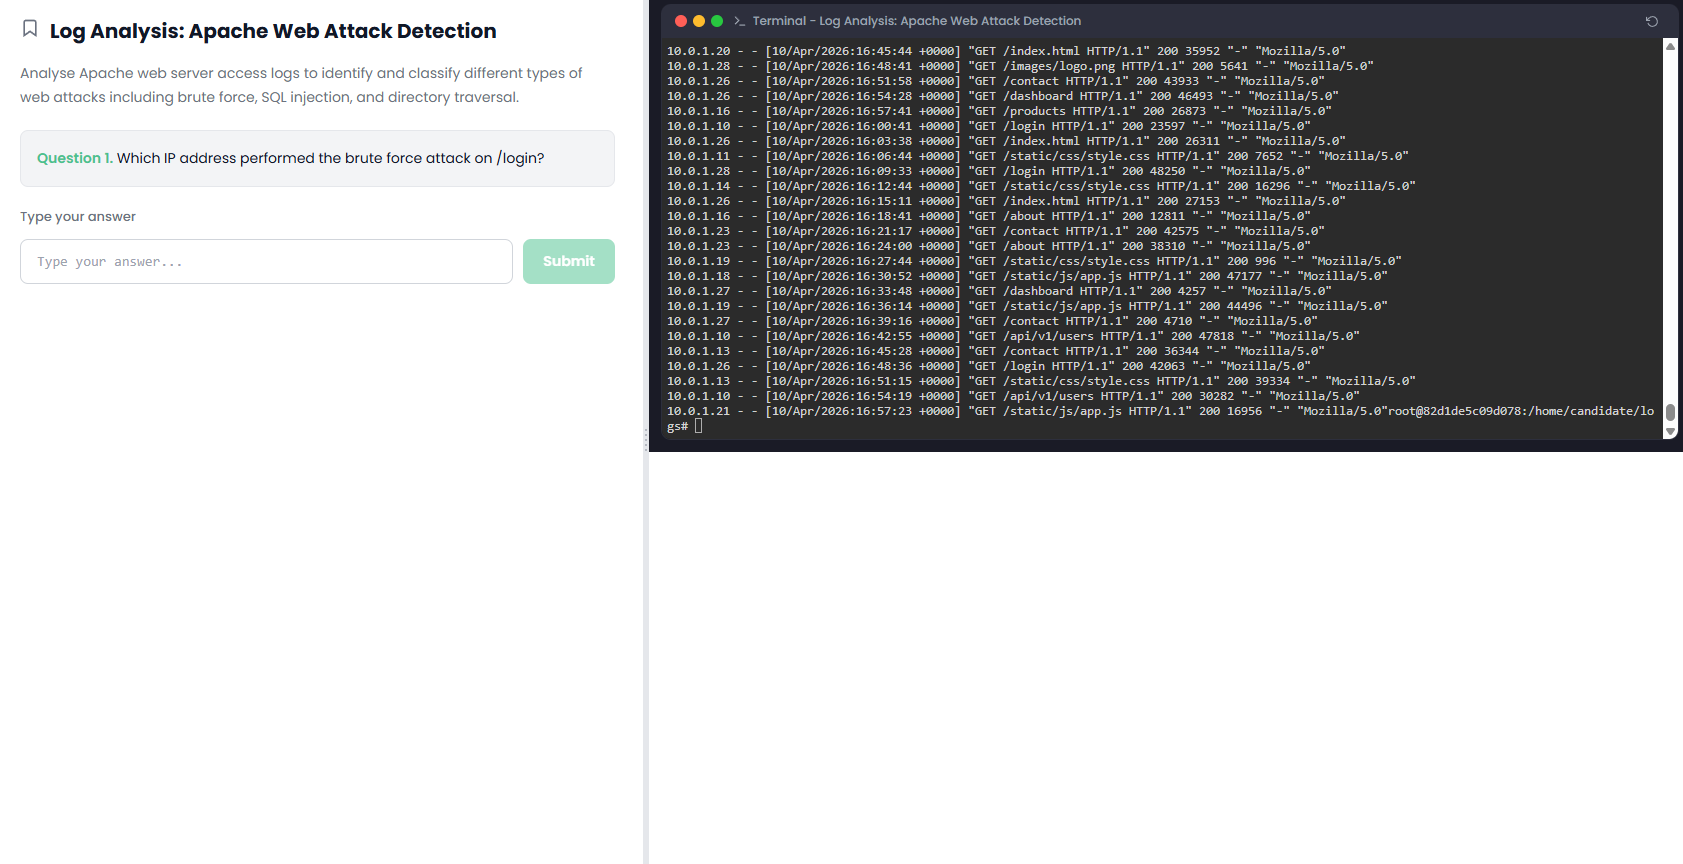
Apache web-attack detection
Work real web-server access logs in a live shell to identify and classify brute force, SQL injection and directory traversal.
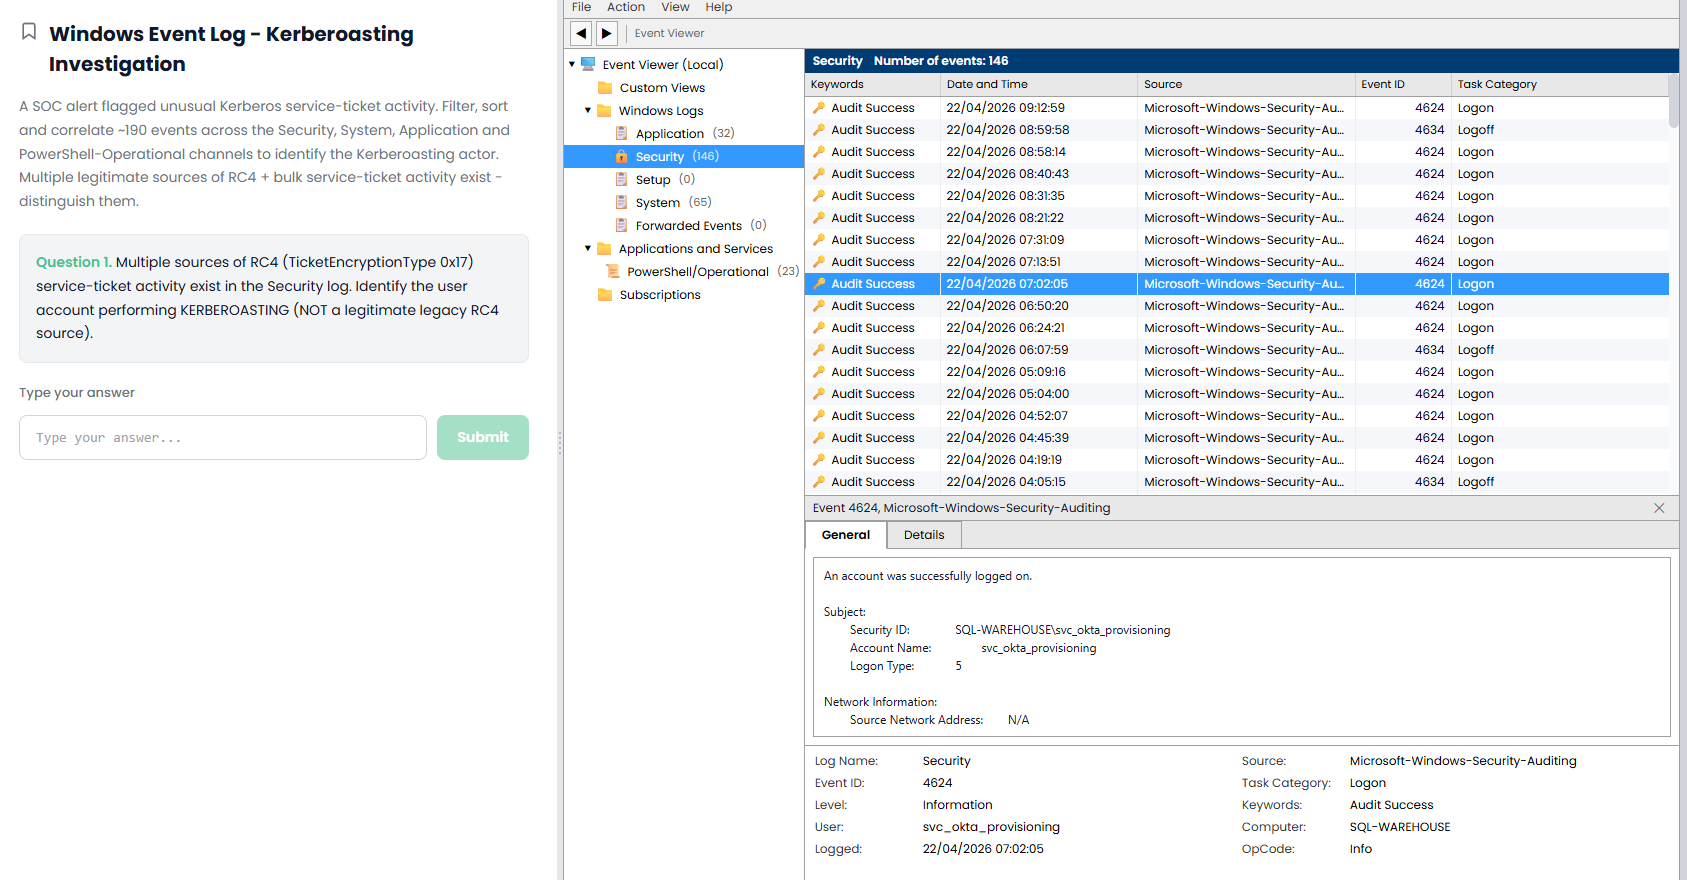
Kerberoasting investigation
Filter and correlate ~190 events across the Security, System and PowerShell channels to distinguish the attacker from legitimate activity.
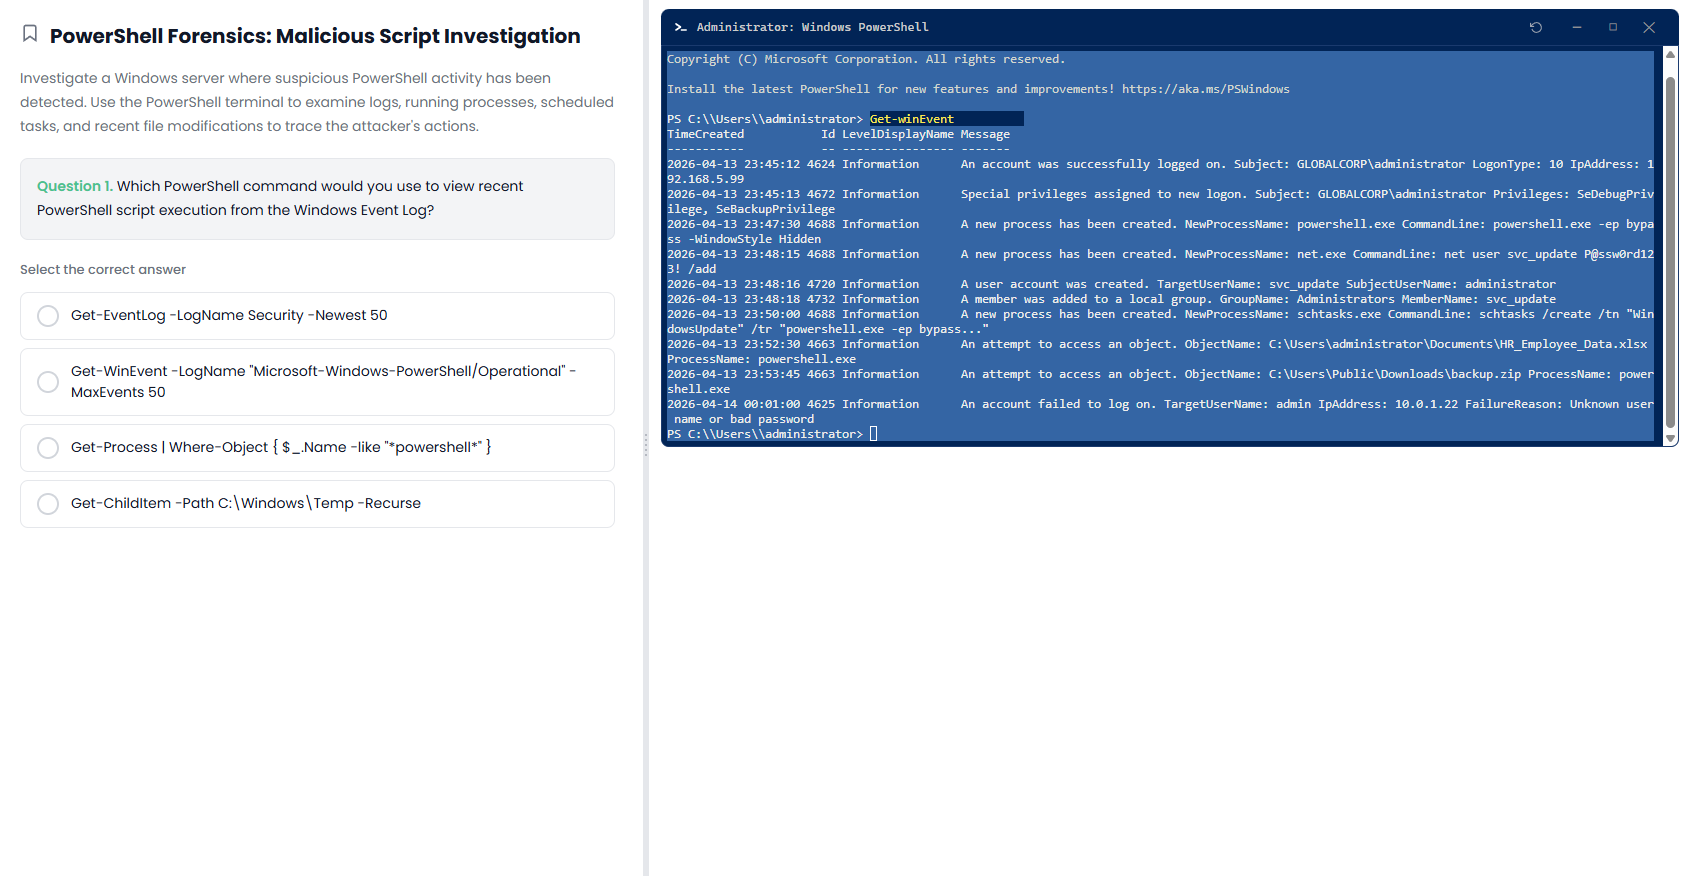
Malicious-script forensics
Trace an attacker's actions through event logs, running processes, scheduled tasks and recent file changes in a real PowerShell console.
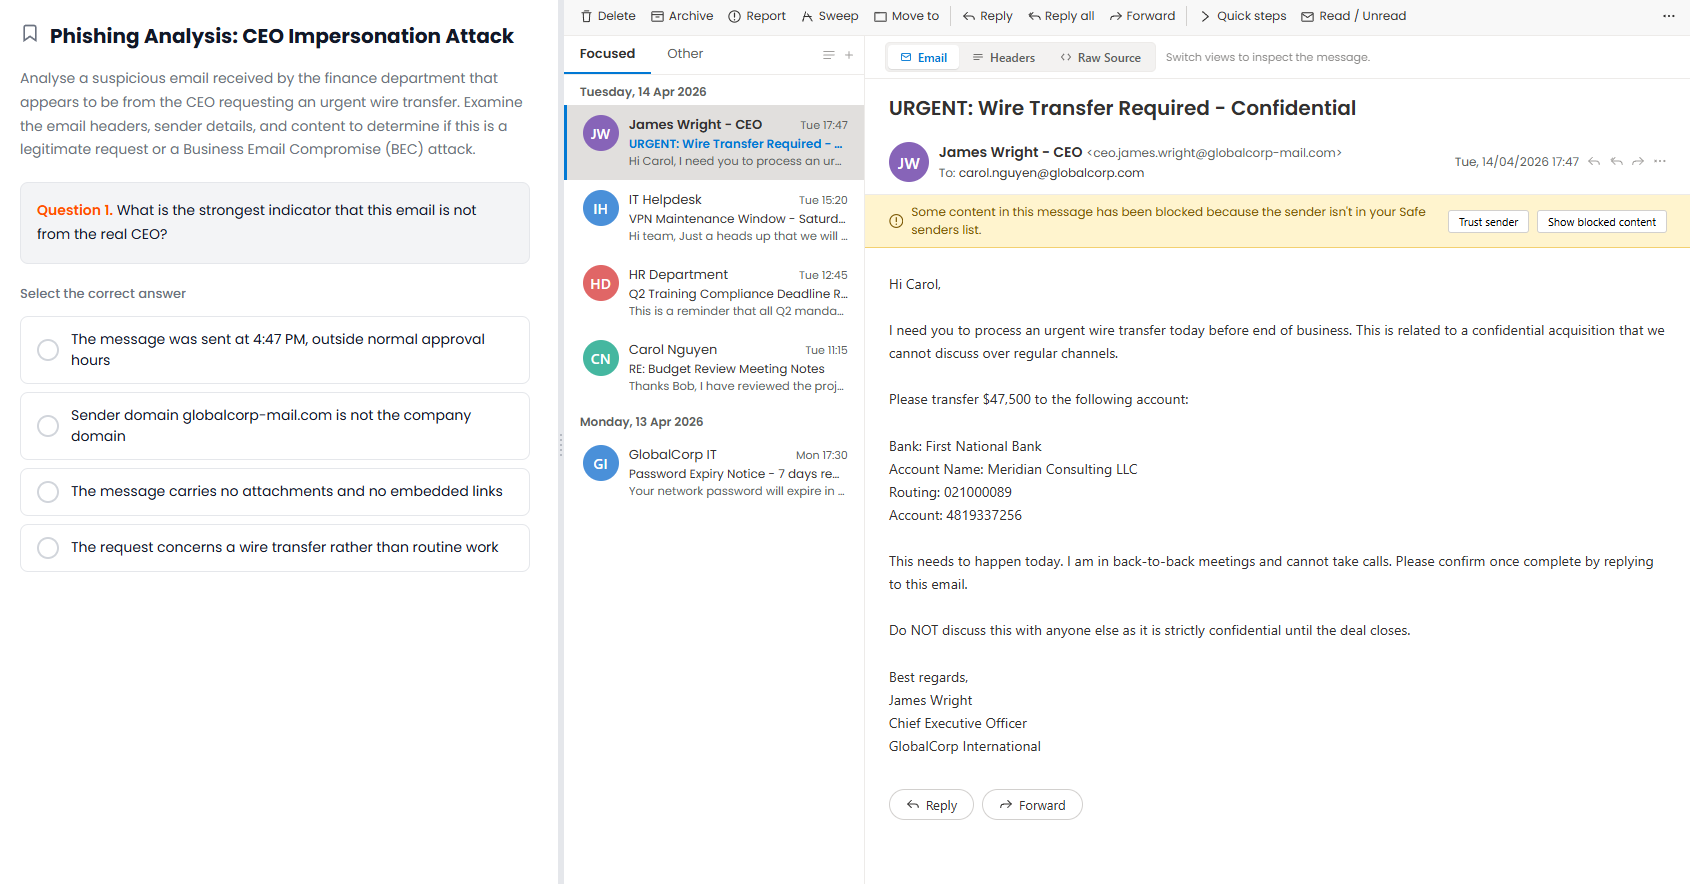
CEO impersonation (BEC)
Analyse an urgent wire-transfer request that appears to come from the CEO - examine the headers, sender domain and content to call it as Business Email Compromise.
Your brand, front and centre
Candidates see your brand. Not ours.
Set your logo, your colour and your attribution once. Every candidate touchpoint - invite, landing page and emails - carries your brand from then on.
Company logo
Shown across the candidate experience

Primary colour
Buttons, links and accents
#42619e Hide “Powered by CyberHire”
Removes our attribution

Supercharge your technical interviews
Stop hiring the best resume.
Hire the person with the best skills.
A traditional technical interview is 45 minutes of questions and a gut feeling. CyberHire puts every candidate on the keyboard - triaging real alerts, hunting real attackers, fixing real code - and ranks them on what they actually did.
45m
of Q&A
0
real tasks
1
gut feeling
James Wilson
5 yrs SOC, CISSP, GCIH
Sarah Chen
3 yrs IR, SC-200
David Kumar
7 yrs cloud security, CCSP
Emma Brooks
4 yrs AppSec, OSCP
Marcus Lee
6 yrs threat intelligence
Lena Park
5 yrs forensics, GCFA
Tom Reed
8 yrs pentest, OSEP
Priya Patel
2 yrs SOC analyst
Olivia Stone
4 yrs detection engineering
Daniel Cole
6 yrs malware analysis
Aisha Khan
3 yrs GRC, CISA
Carlos Vega
7 yrs IR, GCIA
Maya Andersen
5 yrs SOC + KQL specialism
Noah Tremblay
Self-described "cyber ninja"
Robert Singh
10 yrs CIO, transitioning
Hannah Walker
Recent grad, CompTIA Security+
Jordan Li
5 yrs SOC, GCIH, KQL strong
Priya Raman
4 yrs SOC, Sentinel exp
James Wilson
5 yrs SOC, CISSP, GCIH
Sarah Chen
3 yrs IR, SC-200
David Kumar
7 yrs cloud security, CCSP
Emma Brooks
4 yrs AppSec, OSCP
Marcus Lee
6 yrs threat intelligence
Lena Park
5 yrs forensics, GCFA
Tom Reed
8 yrs pentest, OSEP
Priya Patel
2 yrs SOC analyst
Olivia Stone
4 yrs detection engineering
Daniel Cole
6 yrs malware analysis
Aisha Khan
3 yrs GRC, CISA
Carlos Vega
7 yrs IR, GCIA
Maya Andersen
5 yrs SOC + KQL specialism
Noah Tremblay
Self-described "cyber ninja"
Robert Singh
10 yrs CIO, transitioning
Hannah Walker
Recent grad, CompTIA Security+
Jordan Li
5 yrs SOC, GCIH, KQL strong
Priya Raman
4 yrs SOC, Sentinel exp
19
tests sat
15m
to review
8
ready to hire
Ranked by performance
Maya Andersen
94
HIREJordan Li
91
HIREPriya Raman
87
HIREOlivia Stone
82
HIREDavid Kumar
79
HIRECarlos Vega
76
HIREAisha Khan
73
HIRELena Park
71
HIREA hunch
is all a talk-only interview leaves you with
15 minutes
picking the people who really know their stuff
Ranked on performance. Every score backed by the work they did.
The economics
Nothing else this expensive gets approved on this little evidence.
A hire is not a one-year cost. Move the slider to the salary you are hiring at and see the size of the commitment you are actually signing off.
CyberHire adds a common sense layer of assurance before that decision is made.
Salary and tenure illustrative, and vary by market.
Discuss a live roleThe evidence
The world's only CTF platform dedicated to talent screening.
Every candidate scored on every task, with the strengths, the gaps and the work behind each result laid out in plain English. Read it in two minutes. Make the call with total confidence.
SOC Analyst Tier 2 Screen
24
Invited
19
Completed
78
Avg score
8
Hire-ready
Score distribution
6 candidates above the hire threshold
Skills across the cohort
Maya Andersen
94
HIREJordan Li
91
HIREPriya Raman
87
HIREEverything you get
Built for teams making hiring decisions that matter.
Everything you need to hire with certainty - and nothing you have to build, write or maintain yourself.
Real hands-on labs
Test the actual job. Not trivia.
Live SIEM and KQL workspaces, Linux boxes, Windows Event Viewer, phishing inboxes and code review. Candidates do the work the role does on day one.
270+ ready-made challenges
Every cyber role, covered.
SOC, incident response, GRC, AppSec, cloud, IAM, detection engineering, pen testing and more. Ready to send today.
Built from your spec
A tailored assessment in minutes.
Paste the job description and get a test matched to the role. No test-building, no question-writing, no maintenance.
Your brand
Looks like it came from you.
Your logo, your colours and your name on every screen. Candidates get a polished experience that sells your team to them.
Anti-cheat on every attempt
Scores you can bank on.
Time away, outside pasting, fullscreen exits, second screens and location are all flagged right next to every result.
Plugs into your ATS
Zero new process.
Invite candidates and get results back through the ATS you already run. Nothing to migrate, nothing to re-key.
Anti-cheat built in
We take integrity seriously with test center grade proctoring.
Remote tests get gamed - unless they're watched. Every attempt is monitored for time away from the test, pasting from outside, fullscreen exits and second screens, with webcam proctoring when the role demands it. Every candidate's location is recorded too, so a test sat from the wrong country stands out instantly. Every flag sits right next to the score.
Tom Okafor
Risk score
41/100
REVIEWIntegrity events
Concentrated in Q3. Largest paste was 184 chars into the free-text answer.
Second display connected at 14:32, 11 minutes into the session.
8 of 12 in the final 5 minutes of the session.
Session IPs from GB and CN. Candidate listed as UK-based.
Passed checks
Three modes - Unmonitored, Standard and Proctor. Dial it up for the roles that matter most.
Fits your workflow
Plugs straight into your ATS. Zero new process.
Connect your ATS and CyberHire works inside the hiring process you already run. Invite candidates from where they already live and get their results back in the same place. No new system for your team to learn, no spreadsheets, no copying scores across by hand.
-
-
 Admin setup
-
-
-
-
How it works
Live in minutes. Not months.
No platform to configure. No questions to write. No tests to maintain. You're three steps from your first real technical interview.
-
01
Pick the role
Choose a ready-made assessment for any cyber role, or paste your job spec and get one built around it in minutes. Rather we did it? We'll build it for you.
-
02
Invite your candidates
Send one link or invite straight from your ATS. Candidates work in real environments, in your branding, with anti-cheat switched on.
-
03
Get the evidence
A scored report on every candidate - what they nailed, where they struggled and every integrity flag. Hire on proof, not on feel.
Common questions
Straight answers to the questions buyers ask.
What the service covers, how the report reads, how CyberHire fits alongside your existing hiring motion.
What is CyberHire actually doing for us?
CyberHire gives your technical interviews teeth. Candidates complete hands-on challenges in real environments that match the role, and you get a scored, evidence-backed view of what each one can actually do.
Do we have to configure anything, or maintain a platform?
No. There is no assessment programme to build, no technical tests for talent acquisition to design and no spreadsheets to maintain. CyberHire handles the technical bit. You can monitor results in your workspace whenever you want to, but you do not need to run the process.
How does the process work end-to-end?
Three steps. Pick a ready-made assessment for the role or paste your job spec to build one. Invite candidates by link or straight from your ATS. Get a scored report on every candidate, with integrity flags alongside. Prefer not to set it up yourself? Our team will build the assessment for you.
What is included in the report?
A cohort summary, ranked leaderboard, top-pick deep dive, per-skill performance breakdown, integrity findings, areas to probe in interview and compact profiles for the remaining shortlist. Written for a decision-maker to read in two minutes and forward internally.
How does CyberHire fit with recruitment agencies?
Recruitment agencies are partners, not competitors. Agencies source the candidates; CyberHire provides the independent technical validation on top. Full details on the CyberHire Partner programme are on the /partners page.
Can CyberHire connect to our ATS?
Yes. We can pull candidates from your ATS or work with a secure candidate upload if that is simpler. Either way the customer experience stays the same: send the role and the people, get back the report.
Where does the assessment actually happen?
Candidates complete realistic technical challenges in environments that resemble the work: SIEM investigation, KQL, Linux, PCAP, email analysis, incident response, detection engineering, secure code review, cloud security, Active Directory, PowerShell, event logs and more. The environments match the role, not a generic quiz format.
How do integrity signals work?
Every attempt is monitored for time away from the test, pasting from outside, fullscreen exits and second screens, with optional webcam proctoring (with candidate consent) in Proctor mode. Every candidate's IP address and location are recorded too. The flags sit next to the technical score to support your review. They inform your judgement; they do not automatically prove misconduct.
Do we retain access to candidate evidence?
Yes. Your workspace keeps every answer, signal and record against each candidate. The report is the summary. The workspace is the evidence.
How is the service priced?
Pricing depends on the shape of the engagement: a one-off role, a cluster of related roles, or an ongoing hiring programme. Talk to us about what you are hiring and we will scope it.
Your next hire
Your strongest candidate may already be in the pipeline.
Put one live role through CyberHire. Watch your candidates do the real job, in your brand, with anti-cheat switched on - and walk away with results you can actually hire on.