MSSP hiring
One hiring bar for every analyst your MSSP takes on.
Tier 1 SOC, threat hunters, incident responders and malware analysts, across teams and client contracts. Every candidate does the work, in real tools, and is scored the same way, so the bar does not move with whoever ran the interview.
SOC Tier 1 to 3 · Hunting · IR · Malware analysis
Trusted by cyber security teams at


At a glance
How do MSSPs keep one hiring bar across teams?
By putting every candidate for a role through the same hands-on assessment, calibrated to the tier, and scoring it the same way. CyberHire runs that as one programme across every role an MSSP hires for, with role assessments reused from one hire to the next.
- Roles
- SOC analysts at Tier 1, 2 and 3, threat hunters, incident responders, malware analysts, detection, cloud and GRC
- Level
- Tier 1, 2 or 3 per role, so an L1 hire is never screened against an L3 bar
- Consistency
- Same challenges and the same answer key for every candidate for a role, whoever the interviewer is
- Reuse
- Build a role assessment once and reuse it for the next hire, at any site or for any client contract
- Integrity
- Three modes, up to webcam proctoring with consent. Signals sit next to every score.
- Delivery
- A link, a secure bulk upload or straight from your ATS, in your branding.
Why hiring managers use it
Hire across every practice without moving the bar.
Two interviewers, two different shortlists. An MSSP needs the same bar to land on the same candidates, month after month, across every team.
-
The same bar, every candidate.
Automated scoring against one answer key. The candidate a team lead sees has already cleared the same bar as everyone else for that role.
-
Calibrated per role and tier.
An L1 SOC assessment for L1 hires and a senior one for senior hires. Each is built to the level the role needs.
-
Senior time back on the queue.
Every first-round technical interview your seniors skip is time back on client work. They meet candidates who have already shown the work.
-
Reuse, not rebuild.
Role assessments carry over from one hire to the next, so the second SOC hire takes a fraction of the effort of the first.
What candidates work on
Real challenges across the roles an MSSP hires.
A sample from the library. Each role gets its own assessment, built from your job spec at the tier you need.
SOC analysts, Tier 1 to 3
- Phishing Triage - Morning Queue
- SOC Escalation Decisions - Who, When, Why
- Windows Event Log - Kerberoasting Investigation
- KQL Lab: MFA Bypass & Token Replay Detection
Threat hunting and intelligence
- OSINT: Certificate & Domain Intelligence
- Threat Hunting - DNS Beacon Pattern Detection
Incident response
- Ransomware - Hour 1 Containment Decisions
- PowerShell Forensics: Malicious Script Investigation
Malware analysis
- RE: Strings & Symbols (Easy)
- RE: GDB Dynamic Analysis (Medium)
- CyberChef: Malicious PowerShell Deobfuscation
11 challenges · about 256 minutes as listed · trim or swap any of them for your role
Free, before you commit to anything
See it before a candidate does.
Tell us the role. We build a hands-on MSSP assessment for it, in your branding, and send you a private link to sit it yourself. If it is not right for your team, you have lost nothing.
- 01 Tell us the role Send the job spec or just the role title. A job description helps but is not required.
- 02 We build it for you We turn the spec into a hands-on MSSP assessment from real challenges, at the right level, in your branding.
- 03 Invite your applicants You get a private link to try it first. When you are happy, send it to your applicants. That is it.
What you get back
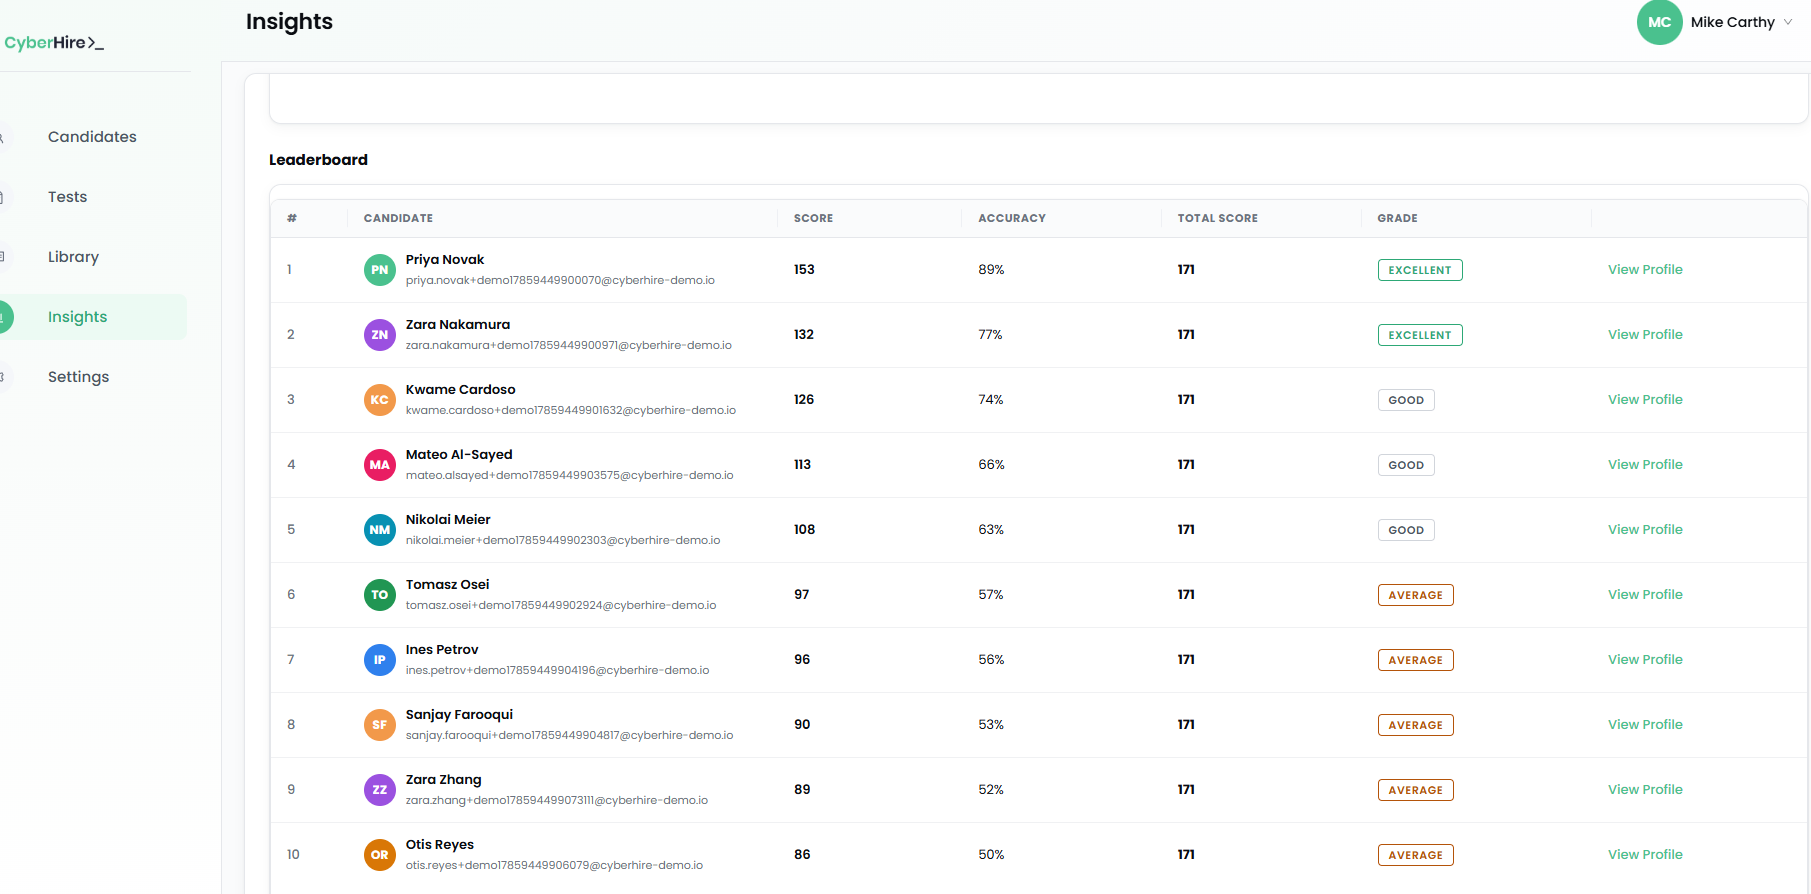
Evidence for every candidate. Read in two minutes.
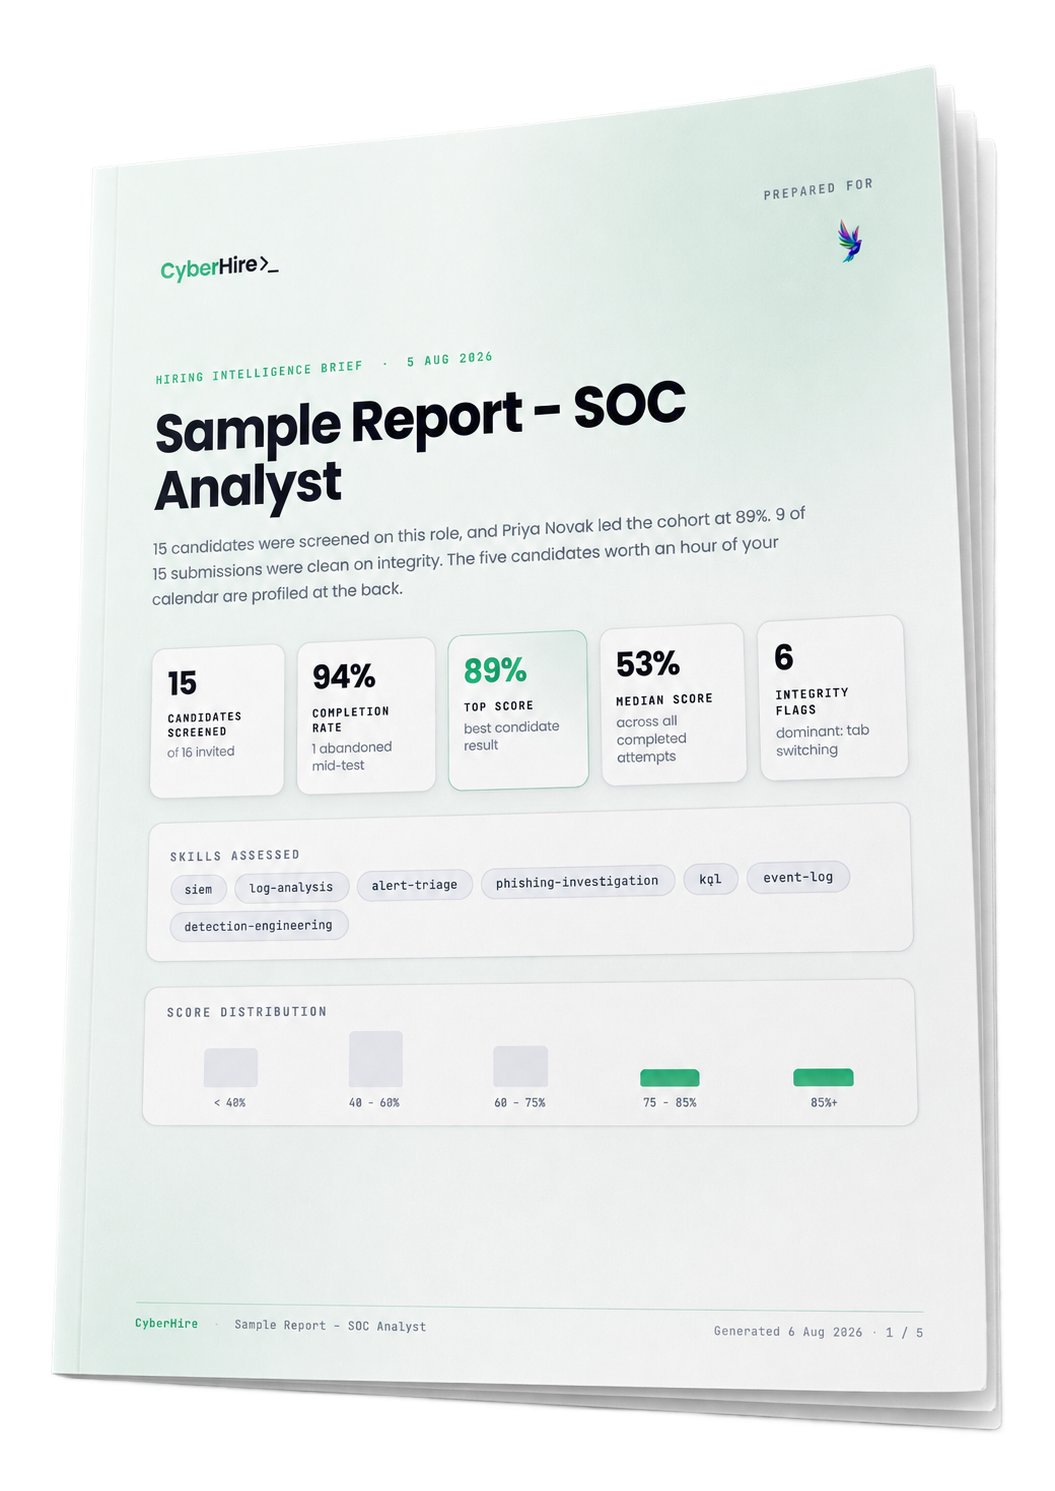
Results arrive in your workspace as candidates finish, and as a hiring report you can forward to anyone on the panel, including people who never log in. Connected to your ATS, the result is written back to the candidate record.
- Ranked, scored the same way Every candidate on the same challenges and the same answer key, ranked on what they did.
- A score per skill Where each candidate is strong and where they are thin, with their actual answers underneath.
- What to probe at interview For every candidate: the skills they were weakest on and the questions behind it.
- Integrity next to every score Time away, outside pasting, fullscreen exits and second screens, flagged for you to weigh.
How it runs
Run hiring as one programme, not a series of one-offs.
- 01
Send us each role
We build an assessment per role and tier from your job specs, in your branding, ready to reuse.
- 02
Invite from anywhere
A link, a secure bulk upload or straight from your ATS. Direct applicants, referrals and agency candidates all sit the same test.
- 03
Candidates do the work
In real environments, in your branding, with integrity monitoring on.
- 04
Every team reads the same evidence
Ranked results, a score per skill and the questions to probe with each candidate, for whichever team lead runs the final interview.
- 05
Reuse for the next hire
The role assessment is ready for the next requisition, at any site or for any client.
Questions we get asked
MSSP hiring questions, answered.
Can different teams use the same assessment?
Yes. A role assessment is built once and reused, so every team hiring for that role, at any site, holds candidates to the same bar.
Can we hire at Tier 1 and Tier 3 at the same time?
Yes. Build one assessment per tier. An L1 hire sits an L1 assessment and an L3 hire sits a senior one, so nobody is judged against the wrong bar.
Does it cover roles beyond the SOC?
Yes. The library covers threat hunting and intelligence, incident response, malware analysis, detection engineering, cloud, application security and GRC, each with hands-on challenges.
How is it priced for an MSSP?
Per role campaign, or as one annual programme sized to the hiring you expect. Talk to us about the roles you hire for and we will size it with you.
Go deeper
The roles MSSPs hire most
None of it is gated.
Try it on your role
Set one bar for every role you hire.
Tell us the roles you hire for. We build the first assessment with you, in your branding, and you try it yourself before any candidate sees it.