The product
The cyber security assessment platform built for hiring.
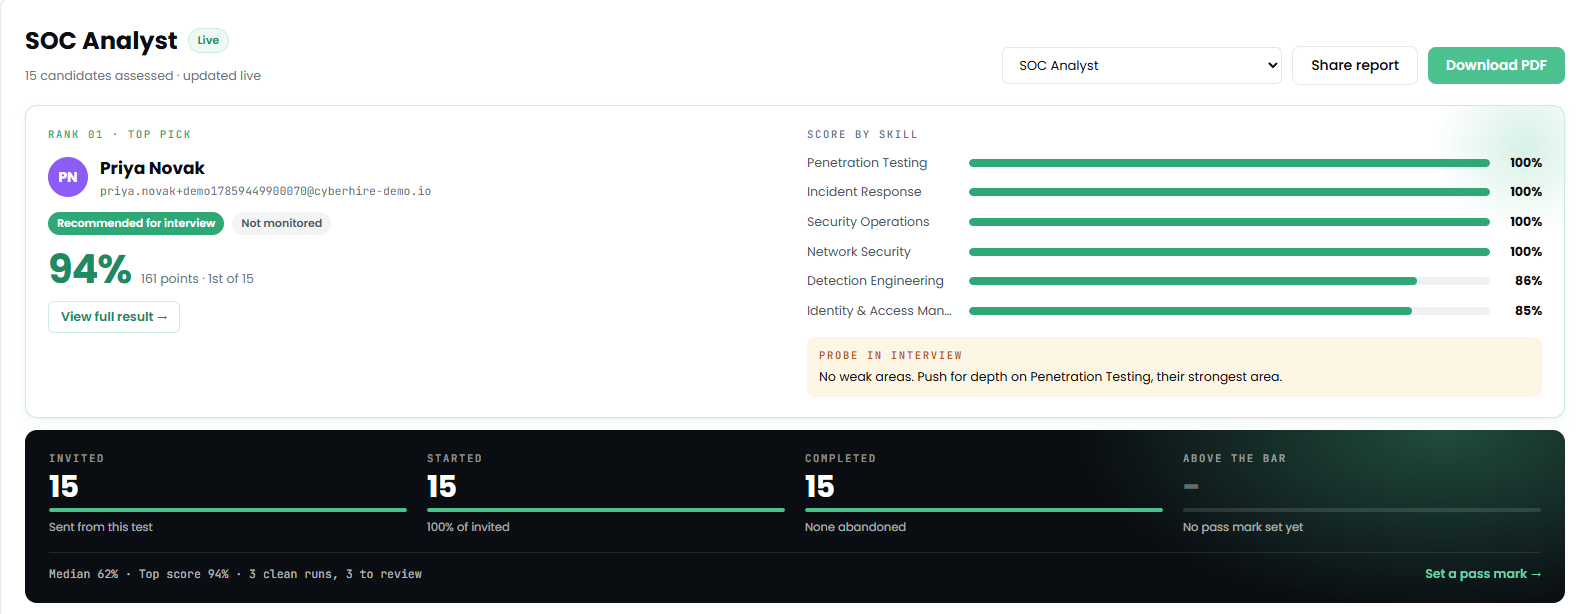
Send us the job spec and we build you a hands-on assessment, ready to go. Invite your applicants, and get ranked evidence for every one of them, with what to probe when you meet them.
270+ challenges · 11 role templates · Tier 1 to 3
Trusted by cyber security teams at


At a glance
What is a cyber security assessment platform?
Software that tests cyber security candidates on hands-on work before they are hired. With CyberHire you send the job spec and we build the assessment for you. Candidates work in real tools on realistic data and every one is scored the same way, so you interview on evidence rather than a CV.
- Setup
- Send us the job spec. We build the assessment for you, in your branding, ready to send.
- Environments
- Live Linux shells, a Sentinel-style KQL workspace, Windows Event Viewer, PowerShell, Group Policy, a mail client, code review, packet captures and live web apps
- Library
- 270+ challenges across SOC, detection, incident response, forensics, cloud, AppSec, IAM, threat intelligence, malware analysis and GRC
- Roles
- 11 ready-made role assessments, or one built for any cyber role from its job spec
- Level
- Tier 1, 2 or 3, or junior to senior. Built to the level you are hiring.
- Scoring
- Automatic, the same way for every candidate, by skill. Written answers are marked blind.
- Integrity
- Three modes, Unmonitored, Standard and Proctor, with signals next to every score
- Integrations
- Invite from your ATS and write results back to the candidate record
- Hosting
- UK and EEA hosting, UK GDPR compliant. A fresh, isolated machine for every candidate.
How it works
You send the spec. We do the rest.
- 01 Send us the job spec Fill in a short form with the role. That is all we need from you.
- 02 We build your test Hands-on, at the right level, in your branding, and ready to send.
- 03 Invite your applicants Send the link, upload a list or invite straight from your ATS.
- 04 Read the evidence Ranked results, a score per skill and what to probe with each candidate at interview.
Done for you
Your test, built for you. Ready to send.
You tell us the role. We turn it into a hands-on assessment and hand it back ready for your applicants. No questions to write, nothing to configure.
What you do
- 1Send us the job spec, or just the role title, through a short form.
- 2Try the test from a private link, if you want to.
- 3Invite your applicants. That is it.
What we do
- Pick the hands-on challenges that match what the role does every day
- Calibrate it to the level you are hiring, Tier 1 to 3 or junior to senior
- Build anything your role needs that the library does not cover
- Set it in your branding and check it before it reaches you
Yours to change in your own workspace, or to send exactly as it is.
The library
Which roles and disciplines does it cover?
We build from 270+ challenges, written and reviewed by security practitioners, each with legitimate activity left in next to the malicious kind. Every role below has a ready-made assessment we tailor to your spec.
Role templates
- SOC analyst
- Security engineer
- Incident response analyst
- GRC analyst
- Cloud security engineer
- Application security engineer
- Detection engineer
- Threat intelligence analyst
- IAM engineer
- Security architect
- Vulnerability management analyst
What candidates can be put in front of
- Log and artefact investigation in a live Linux shell
- Sentinel-style KQL hunting against realistic telemetry
- Phishing triage with full headers and raw source
- Windows event log and registry forensics
- Packet capture analysis for C2 and exfiltration
- Secure code review in Python, Java, JavaScript and Go
- Live web applications to exploit
- Cloud: Terraform and IAM policy review on AWS and GCP
- Group Policy and firewall configuration review
- Detection tuning: Sigma rule triage and noisy rules
- Reverse engineering and malware triage
- GRC: vendor reports, risk registers and control mapping
The candidate's screen
What do candidates actually do?
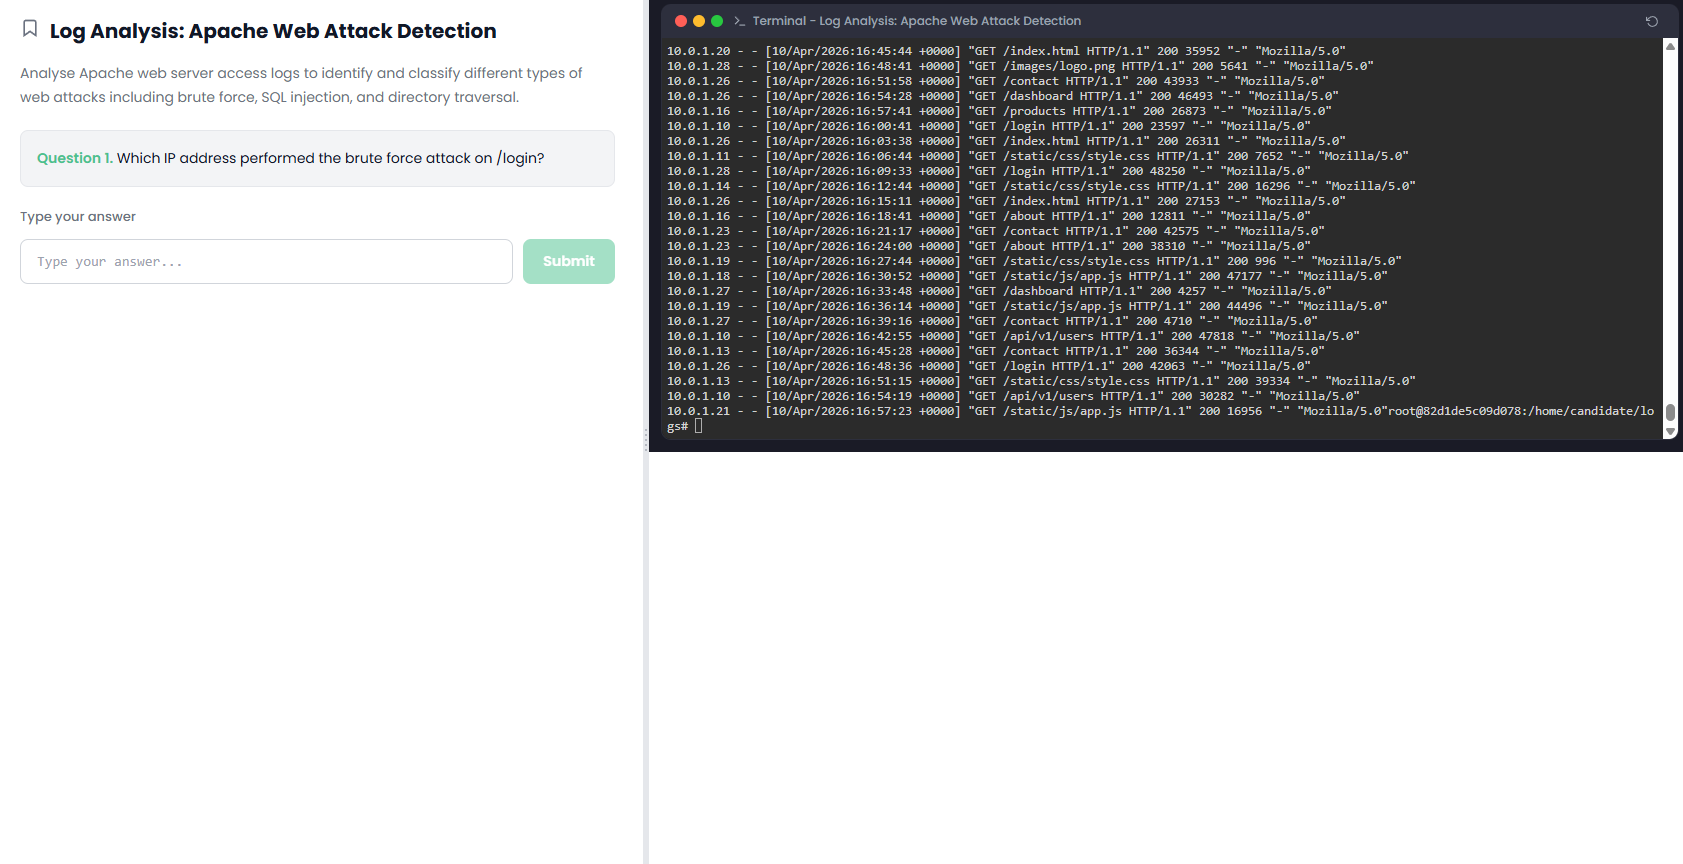
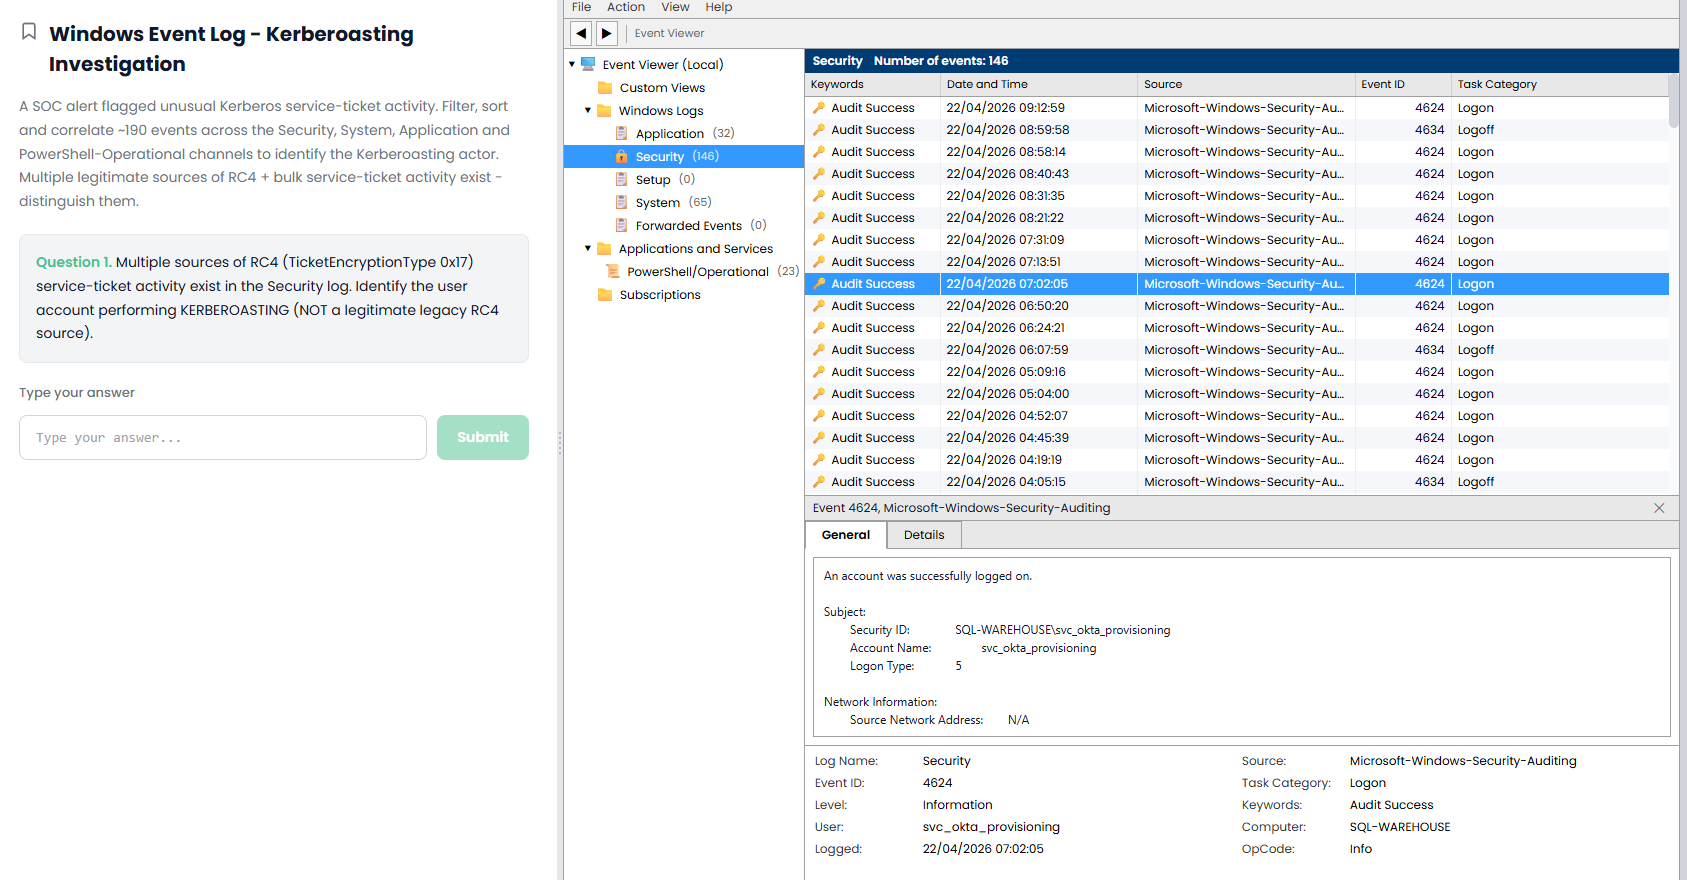
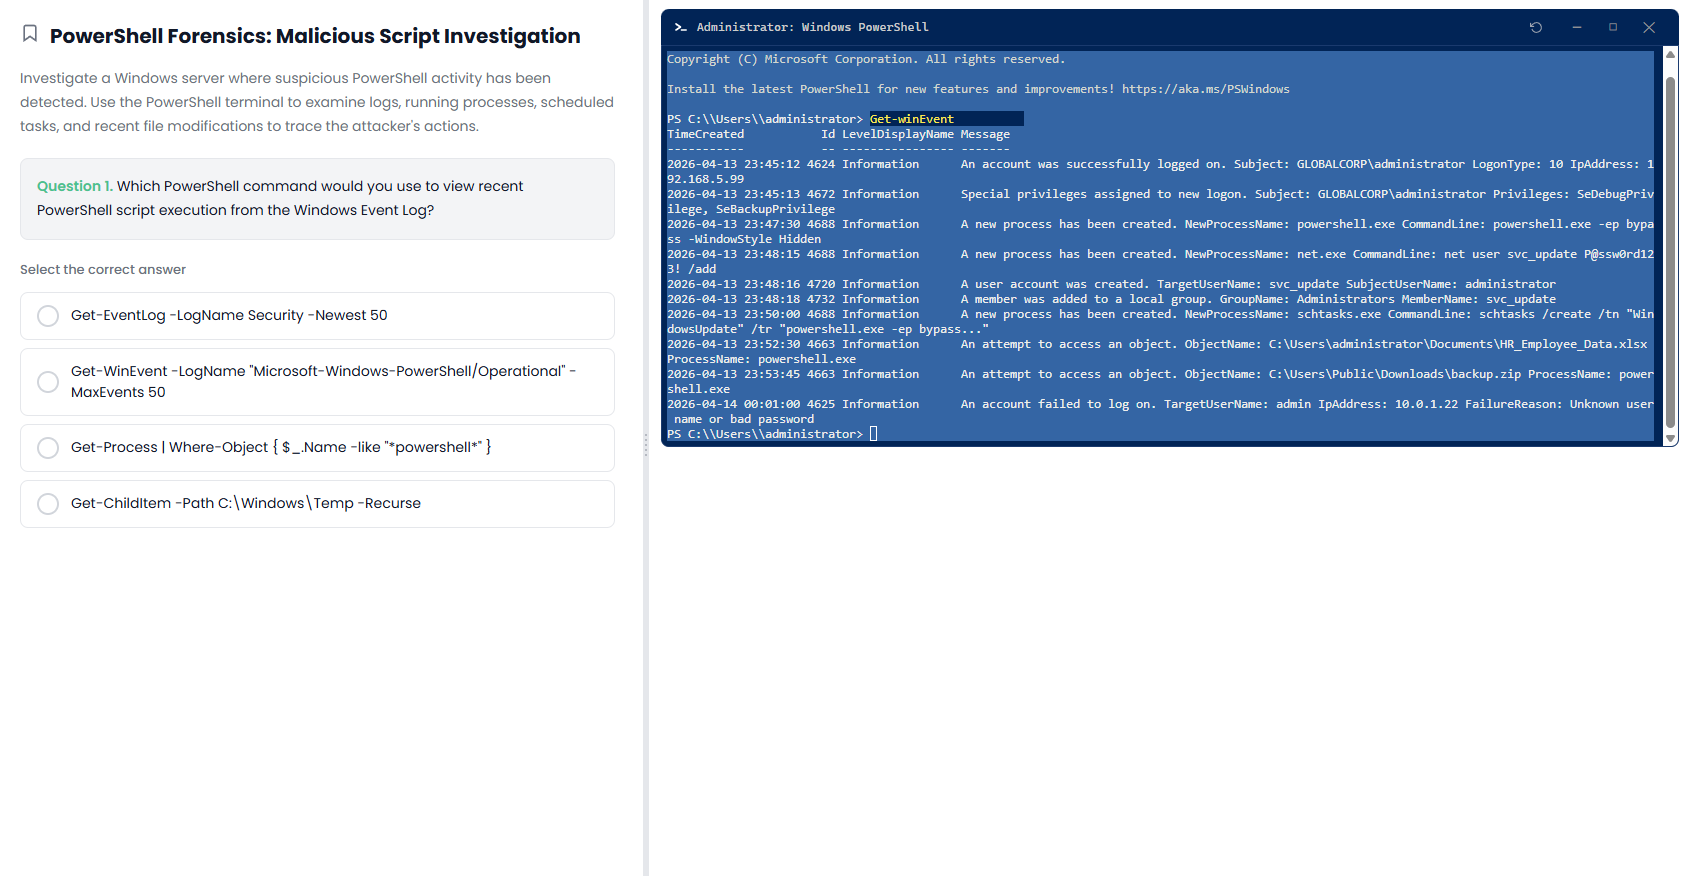
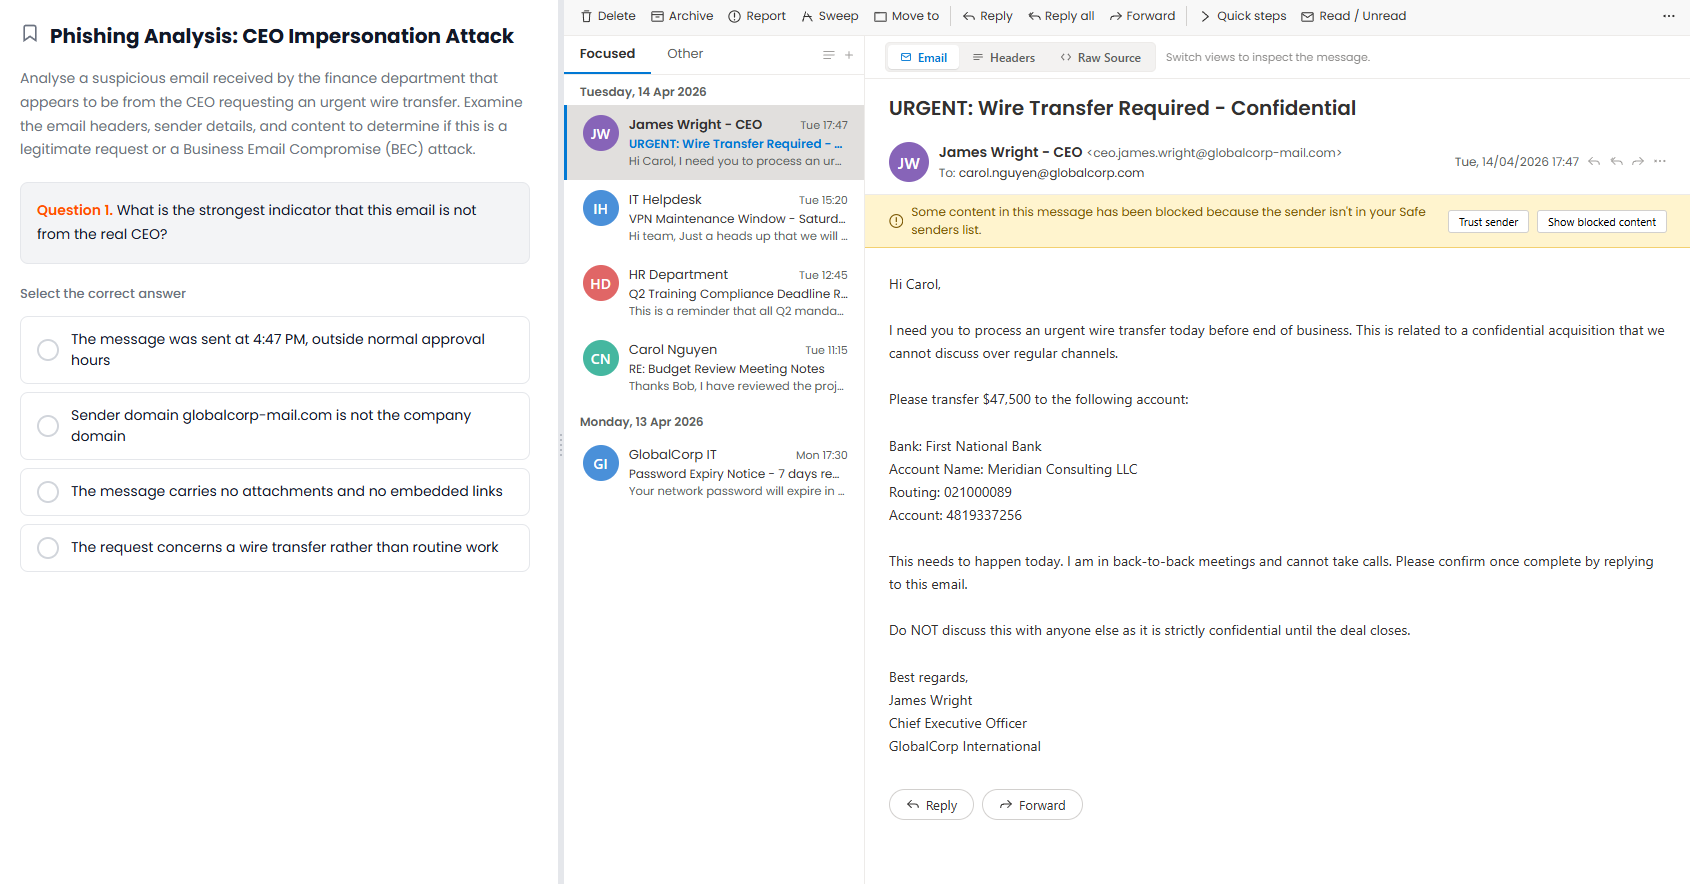
The work, in the tools. They triage phishing in a mail client, investigate in Windows Event Viewer, hunt in a Sentinel-style KQL workspace and work in a live Linux shell. These are real screens from the product.
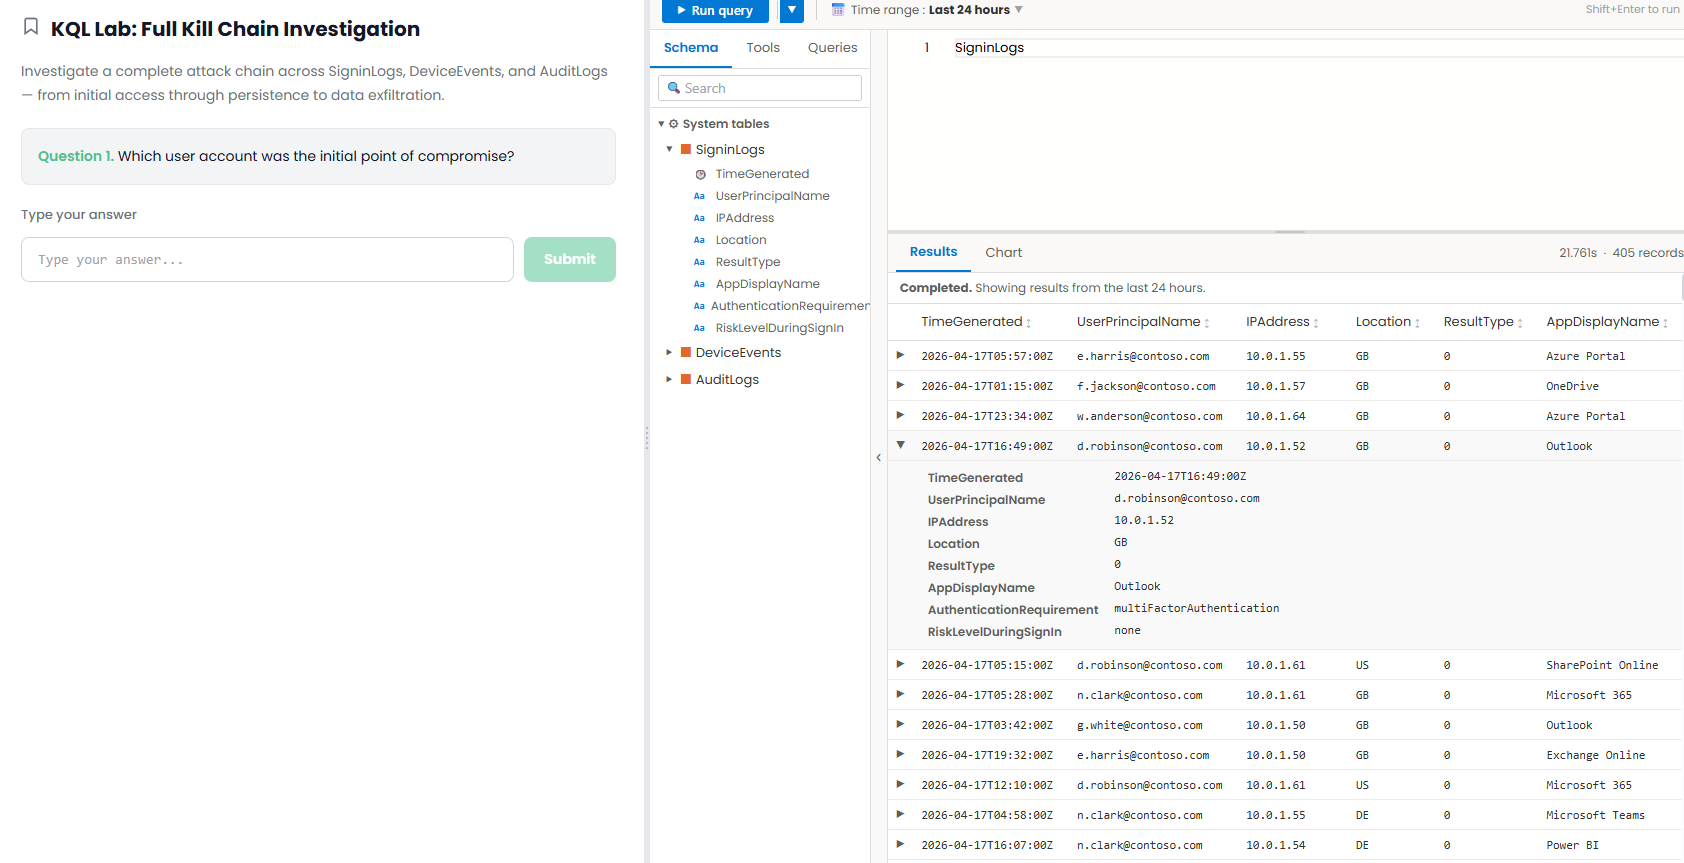
Full kill-chain investigation
Hunt a live attack across SigninLogs, DeviceEvents and AuditLogs - from initial access through persistence to exfiltration.
Apache web-attack detection
Work real web-server access logs in a live shell to identify and classify brute force, SQL injection and directory traversal.
Kerberoasting investigation
Filter and correlate ~190 events across the Security, System and PowerShell channels to distinguish the attacker from legitimate activity.
Malicious-script forensics
Trace an attacker's actions through event logs, running processes, scheduled tasks and recent file changes in a real PowerShell console.
CEO impersonation (BEC)
Analyse an urgent wire-transfer request that appears to come from the CEO - examine the headers, sender domain and content to call it as Business Email Compromise.
In your branding
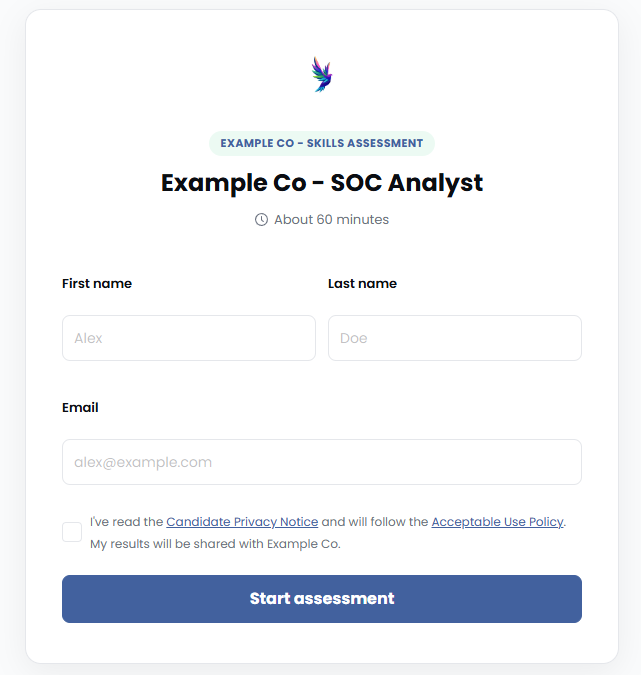
Candidates see your logo and your colours from the first screen, so the assessment feels like part of your hiring process, not a third party's.
Integrity
How does CyberHire stop cheating?
Mostly by task design: the answers sit in data only the candidate can see. Then three modes. Standard records time away from the test, outside pasting, fullscreen exits and second screens. Proctor adds video proctoring, with the candidate's consent. Location is recorded in every mode.
No assessment catches everything, and we will not claim ours does. What it catches, it catches consistently, and every signal sits next to the score as evidence for you to weigh, never an automatic rejection.
Tom Okafor
Risk score
41/100
REVIEWIntegrity events
Concentrated in Q3. Largest paste was 184 chars into the free-text answer.
Second display connected at 14:32, 11 minutes into the session.
8 of 12 in the final 5 minutes of the session.
Session IPs from GB and CN. Candidate listed as UK-based.
Passed checks
The evidence
What do you see when a candidate finishes?
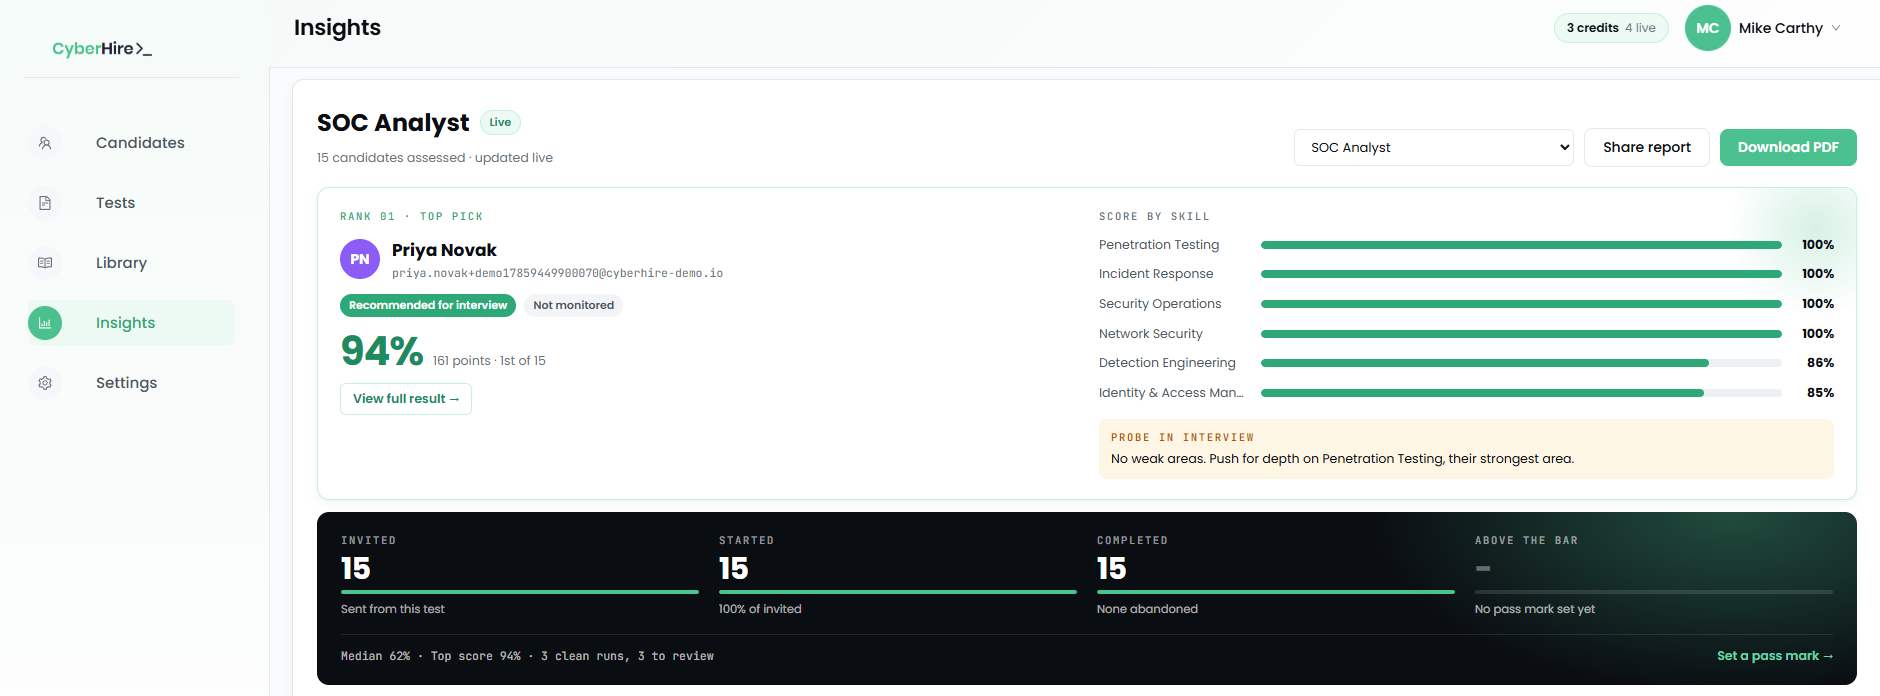
- Ranked, scored the same way Every candidate on the same challenges and answer key, ranked on what they did, with time taken.
- A score per skill Where each candidate is strong and where they are thin, with their actual answers underneath.
- What to probe at interview For every candidate: the skills they were weakest on and the questions behind it.
- Calibrated to the level Every test carries the tier it was built for, so a score is read against the right bar.
- Written answers marked blind Free-text answers are marked without the candidate's name, and never counted as wrong while unmarked.
- A report anyone can read A hiring report to forward to the panel, including people who never log in.
Fits your workflow
Does it work with your ATS?
Yes. Invite candidates from your ATS and the result is written back to the candidate record. Or skip the integration and send a link or a secure bulk upload.
-
-
 Admin setup
-
-
-
-
Bought per role or as an annual programme · No recurring commitment for a single role
Security and data
How is candidate data protected?
- UK and EEA hosting UK GDPR compliant, with a data processing addendum and a published list of sub-processors.
- A fresh machine per candidate Every candidate gets their own isolated environment in London. Nothing one candidate does is visible to the next.
- Integrity, with consent Video proctoring only in Proctor mode and only with the candidate's consent, covered by a published DPIA.
- Retention you can state Assessment results are kept for 24 months and video proctoring data for 90 days, then deleted.
Read the data processing addendum, sub-processors and integrity monitoring DPIA.
Why teams pick us
Built for cyber hiring. Nothing generic.
Better capability. More credibility.
Hire people who can actually triage, query, reverse and respond, shown on real work before the offer rather than discovered months after it.
Built for cyber. Nothing generic.
SOC, cloud, AppSec, incident response and more, in real environments. Send us the job spec and we build the assessment for you, ready to send.
See the work first. Interview with evidence.
Candidates take the assessment on their own time. You get scores, the work behind them and integrity signals, so interview time goes to the people worth meeting and to the right questions.
You wouldn't hire a pilot without a test flight.
Your security team is flying your entire operation. When it crashes and burns, the cost is measured in regulatory fines, breach disclosures, and a very awkward board meeting. Put them in the simulator first.
Regulators want proof.
Every serious framework wants documented evidence your security team can actually do the job.
People deserve a fair shake.
We believe in fairness. Your filters are quietly rejecting hidden gems. The self-taught analyst. The career-switcher. The one without the university logo. Skill-first testing drags them back in.
A hiring decision you can defend.
Every candidate scored on the same assessment, against the same baseline, with the same evidence trail attached. Your reviewers make the call, and the "why this hire?" question is answered before anyone asks it.
Questions buyers ask
Before you choose a vendor.
What is a cyber security assessment platform?
Software that tests cyber security candidates on hands-on work before they are hired: investigating logs, hunting in a SIEM, reviewing configuration and code, in environments that look like the job. With CyberHire you send the job spec, we build the assessment, and every candidate is scored the same way.
How is it different from a training lab or a CTF?
Training labs and CTFs are built for learning and practice, and their answers are often published. A hiring assessment is built for a decision: it is calibrated to the role and level, scored the same way for every candidate, monitored for integrity and reported in a form a hiring panel can act on.
How do you stop cheating and AI-assisted answers?
Mostly by task design: the answers sit in data only the candidate can see, so there is little a model can answer from general knowledge. Standard mode records time away from the test, outside pasting, fullscreen exits and second screens; Proctor mode adds video proctoring with consent; location is recorded in every mode. No assessment catches everything, and we do not claim to. Flags are evidence for you to weigh, never an automatic rejection.
Does it work with our ATS?
Yes. Connect your ATS to invite candidates from it and have results written back to the candidate record. The tested integrations are shown above, and the integration provider covers more than 60 recruiting platforms. A link or secure bulk upload works without any integration.
Where is candidate data held?
UK and EEA hosting, UK GDPR compliant. The data processing addendum, sub-processor list and integrity monitoring DPIA are published, and results are kept for 24 months.
What do we need to do?
Very little. Fill in a short form with the role and send the job spec if you have one. We build the assessment, in your branding, and send you a private link to try it. When you are happy, invite your applicants.
Can we change the assessment ourselves?
Yes. It is yours once we hand it over: swap challenges, change the length or the level, or adjust the settings in your own workspace. Most teams send it as it is.
How is CyberHire bought?
Per role, as a campaign for one hire, or as an annual programme if you hire continuously. There is no recurring commitment for a single role. The simplest start is a free assessment built for one of your live roles.
Who writes the challenges?
The library is written and reviewed by security practitioners, and every challenge puts legitimate activity next to the malicious kind, because separating the two is the job. When your role needs something the library does not cover, we build it.
Free, with no commitment
Send us the job spec. Get a test ready to go.
Tell us the role in a short form. We build a hands-on assessment for it, in your branding, and send you a private link to try it. It is free, there is no commitment, and if it is not right for your team, you have lost nothing.
Free · Built in your branding · Ready to send · No commitment