GRC analyst hiring
Hire GRC analysts who find the gaps before the auditor does.
Give candidates the documents the job runs on: a vendor's assurance report, a risk register, a policy bundle and a control mapping. See who reads carefully, spots what is missing or wrong, and can explain the risk.
Junior, mid-level or senior · Real documents · Built from your job spec
Trusted by cyber security teams at


At a glance
What is a GRC analyst skills assessment?
A GRC analyst skills assessment is a hands-on review of the documents the role works with: vendor assurance reports, risk registers, policies and control mappings. Candidates find the gaps and weaknesses an auditor would, and say why they matter, before anyone is interviewed.
- Work
- Vendor SOC 2 reports and questionnaires, risk registers, policy bundles, system architectures and control mappings
- Frameworks
- ISO 27001, SOC 2, NIST 800-53 and NIST CSF in the ready-made assessment; PCI DSS, HIPAA and UK GDPR work in the library
- Level
- Junior, mid-level or senior. Tell us the level and we build it to that difficulty.
- Length
- Sized to your process. The ready-made assessment is six challenges, a little over two hours; a first screen needs two or three.
- Scoring
- Automatic, against the same answer key for every candidate, broken down by skill.
- Integrity
- Three modes, up to webcam proctoring with consent. Signals sit next to every score.
- Delivery
- A link, a secure bulk upload or straight from your ATS, in your branding.
Why hiring managers use it
Hire for careful reading, not framework recall.
Most candidates can name the ISO 27001 clauses. Far fewer can read a vendor's SOC 2 report and notice that the exception that matters to you is buried in the testing results.
-
Review skill you can see.
Candidates work through real documents written with the kinds of gaps that matter. You see who is thorough, and exactly where each candidate missed something.
-
Judgement, not just knowledge.
Telling a meaningful risk from a cosmetic one, and a treatment that works from one that only looks tidy, is the job. The assessment tests it directly.
-
Weighted to your compliance landscape.
We build it from your job spec, leaning towards the frameworks you work to. Your GRC lead writes nothing and marks nothing.
-
Fair to unconventional backgrounds.
Everyone reviews the same documents under the same conditions, so a careful reader from audit, risk or operations gets the same chance as someone with the perfect CV.
What candidates work on
The ready-made GRC analyst assessment.
Six hands-on reviews across third-party risk, risk management and control frameworks, set at mid-level. We tailor it to your job spec, from the documents to the length and level.
Third-party risk
- Vendor SOC 2 Type II Review - AcmePayroll Inc.
- Vendor Risk Assessment: SaaS HR Platform
Risk management
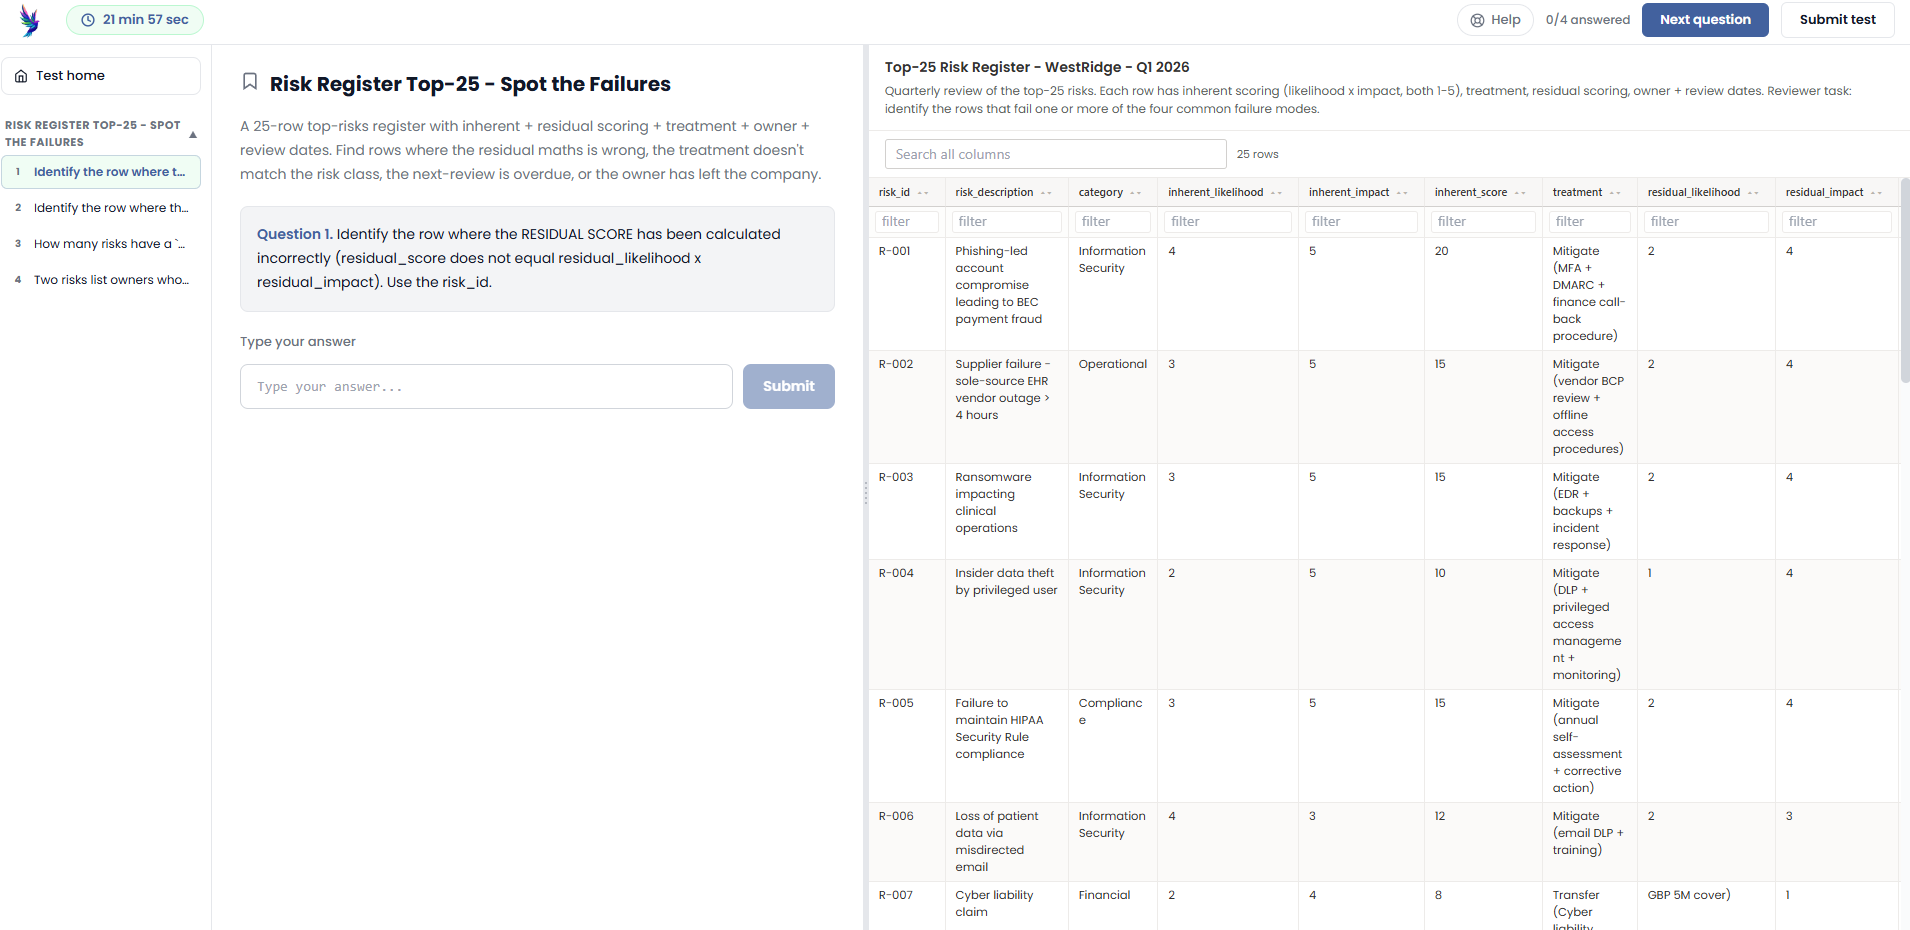
- Risk Register Top-25 - Spot the Failures
Frameworks and controls
- ISO 27001 Gap Analysis - Policy Bundle Review
- NIST 800-53 Control Mapping - System Architecture Review
- Multi-Framework Control Crosswalk - ISO 27001 / SOC 2 / NIST CSF
6 challenges · about 133 minutes as listed · trim or swap any of them for your role
One case, end to end
What a strong answer actually looks like.
A 25-row top-risks register prepared for a quarterly review, with inherent and residual scoring, treatments, owners and next-review dates. Find the rows that would not survive an audit.
Checks the scoring rather than trusting it, questions whether each treatment can actually work for that kind of risk, catches the reviews that have lapsed and the owners who are no longer with the company, and types the risk IDs. There is no list to pick from.
Reads the register for its content and agrees with it, missing the process failures: the score that does not add up and the review dates already in the past.
Free, before you commit to anything
See it before a candidate does.
Tell us the role. We build a hands-on GRC analyst assessment for it, in your branding, and send you a private link to sit it yourself. If it is not right for your team, you have lost nothing.
- 01 Tell us the role Send the job spec or just the role title. A job description helps but is not required.
- 02 We build it for you We turn the spec into a hands-on GRC analyst assessment from real challenges, at the right level, in your branding.
- 03 Invite your applicants You get a private link to try it first. When you are happy, send it to your applicants. That is it.
What you get back
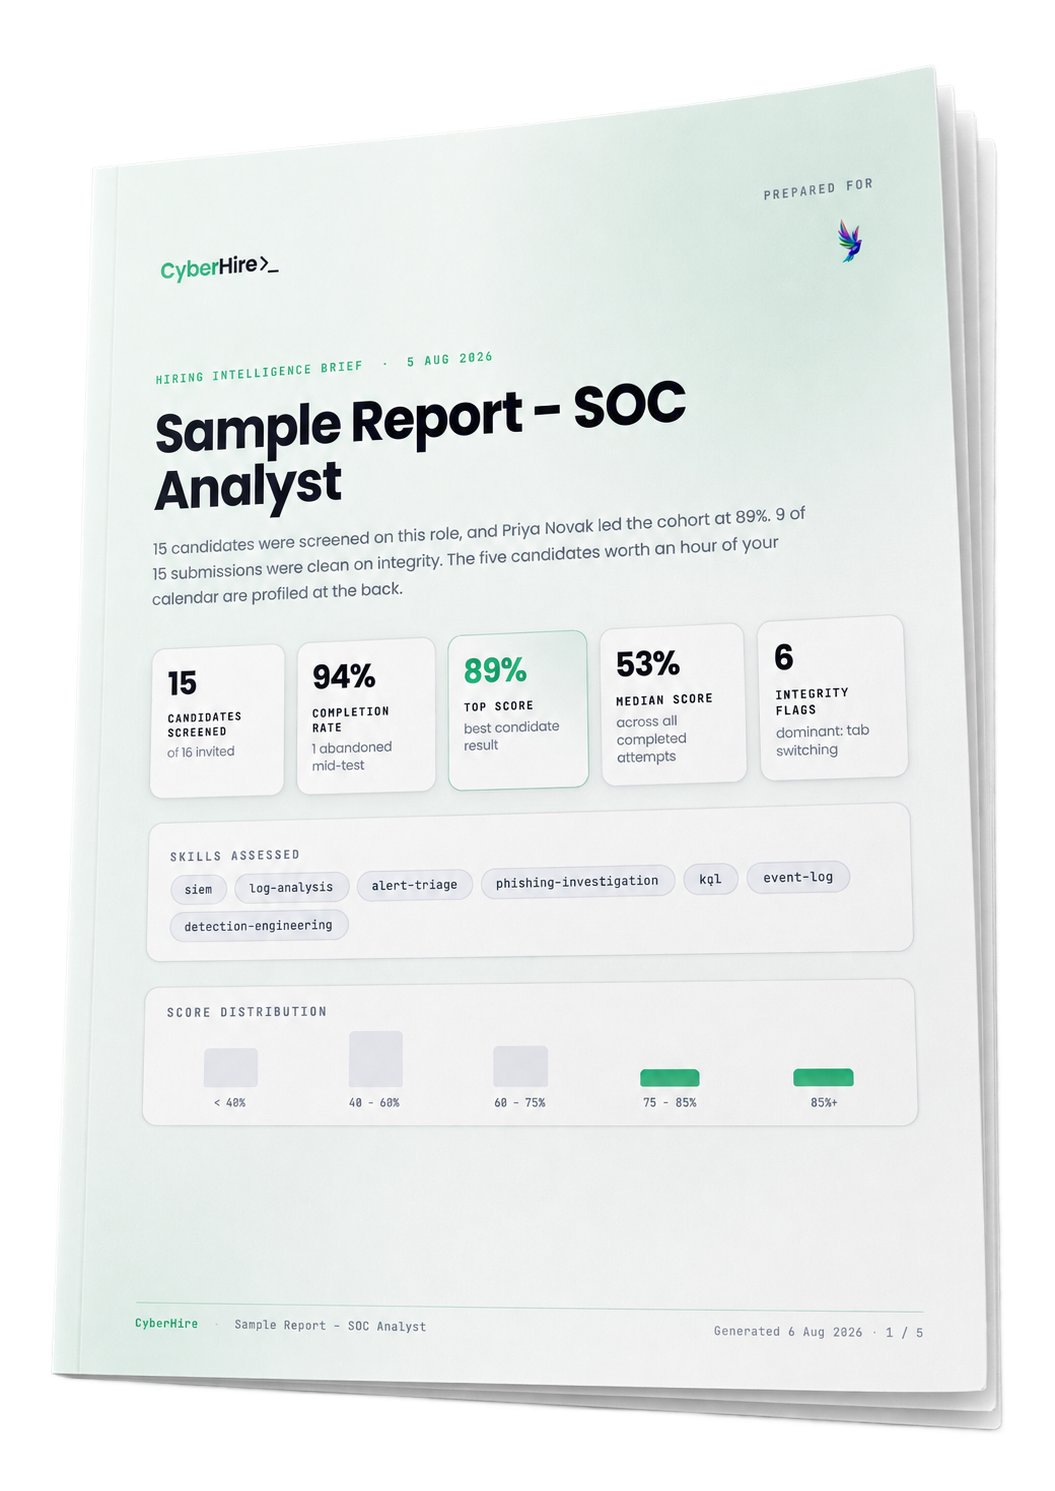
Evidence for every candidate. Read in two minutes.
Results arrive in your workspace as candidates finish, and as a hiring report you can forward to anyone on the panel, including people who never log in. Connected to your ATS, the result is written back to the candidate record.
- Ranked, scored the same way Every candidate on the same challenges and the same answer key, ranked on what they did.
- A score per skill Where each candidate is strong and where they are thin, with their actual answers underneath.
- What to probe at interview For every candidate: the skills they were weakest on and the questions behind it.
- Integrity next to every score Time away, outside pasting, fullscreen exits and second screens, flagged for you to weigh.
How it runs
From job spec to evidence you can act on.
- 01
Send us the role
Fill in the form with the job spec, or just the role title. That is all we need from you.
- 02
We build your assessment
Hands-on, built to your role and level, in your branding, and ready to send. Change anything you like, or send it exactly as it is.
- 03
Invite candidates
A link, a secure bulk upload or straight from your ATS. Everyone reviews the same documents.
- 04
Candidates do the work
In a document viewer and data tables, in your branding, with integrity monitoring on.
- 05
Read the evidence
A ranked cohort, a score per skill, the questions to probe with each candidate and any integrity signals.
Questions we get asked
GRC hiring questions, answered.
How do you assess a GRC analyst's skills?
Give them the documents the role works with, such as a vendor SOC 2 report, a risk register or a policy bundle, and ask them to find the gaps and explain the risk. Score the findings, then use the interview to explore how they would raise and resolve them.
Is a practical test fair for GRC roles?
Yes, and often fairer than a CV screen. Every candidate reviews the same documents under the same conditions, so people with less conventional backgrounds can show the same careful reading as anyone else.
Which frameworks does it cover?
The ready-made assessment covers ISO 27001, SOC 2, NIST 800-53 and NIST CSF, including a crosswalk between them. The library also has PCI DSS, HIPAA and UK GDPR work. We build from your job specification, weighted to the frameworks you work to.
How long does it take?
As long as suits your process. The ready-made assessment is six reviews of 15 to 28 minutes each. For a first screen, two or three are enough to see who reads carefully.
Do we still need to interview?
Yes. The assessment shows who can do the review work. The interview then goes on how they would raise findings with the business, and the areas the assessment flagged.
Go deeper
How we think about GRC assessment
None of it is gated.
Try it on your role
See the GRC analyst assessment built for your role.
Send us the job spec. We build the assessment around it, in your branding, and you try it yourself first. Free, and with no commitment.