Security engineer hiring
Hire security engineers who can find the weak control.
Put candidates in front of the controls the job owns: a live firewall ruleset, a domain's Group Policy, a Linux host and a packet capture. See who finds what is wrong, explains why it matters and makes the right call on a change.
Junior, mid-level or senior · Live configs, real tools · Built from your job spec
Trusted by cyber security teams at


At a glance
What is a security engineer technical assessment?
A security engineer technical assessment is a hands-on review of the controls the role will own, such as firewall rules, Group Policy, host hardening and network traffic. Candidates find the weaknesses in real configurations and decide what to change, before anyone is interviewed.
- Environments
- Live Linux shell, Group Policy Management console, firewall rule sets and configs, packet captures
- Level
- Junior, mid-level or senior. Tell us the level and we build it to that difficulty.
- Length
- Sized to your process. The ready-made assessment is six challenges, about two hours; a first screen needs two or three.
- Answers
- Findings typed from the configuration in front of them, plus approve-or-reject change decisions.
- Scoring
- Automatic, against the same answer key for every candidate, broken down by skill.
- Integrity
- Three modes, up to webcam proctoring with consent. Signals sit next to every score.
- Delivery
- A link, a secure bulk upload or straight from your ATS, in your branding.
Why hiring managers use it
Test the version of the job you actually have.
One organisation's security engineer runs firewalls and endpoint policy. Another's writes infrastructure code. The CV lists every tool either way. The assessment shows which job the candidate can do.
-
Configuration skill you can see.
Describing least privilege is easy. Spotting the rule that quietly exposes a database is the job, and here the candidate does it in front of you, in a live shell and a real Group Policy console.
-
Change judgement, tested.
An emergency firewall change lands. Approve or reject? The decisions a good engineer makes under pressure are tested directly, not discussed hypothetically.
-
Built from your job spec.
Send the spec and we build the assessment around it, weighted to network, endpoint policy or Linux hardening to match the role. Your engineers write nothing and mark nothing.
-
A sharper final interview.
Every candidate arrives with a score by skill and the questions they missed, so the interview goes on design trade-offs and how they handle change.
What candidates work on
The ready-made security engineer assessment.
Six hands-on challenges across the controls the role owns, set at mid-level. We tailor it to your job spec, from the challenges to the length and level.
Network security and firewalls
- Emergency Firewall Change - Approve or Reject
- Firewall Rule Analysis & Network Segmentation
- PCAP: DNS Tunneling Detection
Windows and Group Policy
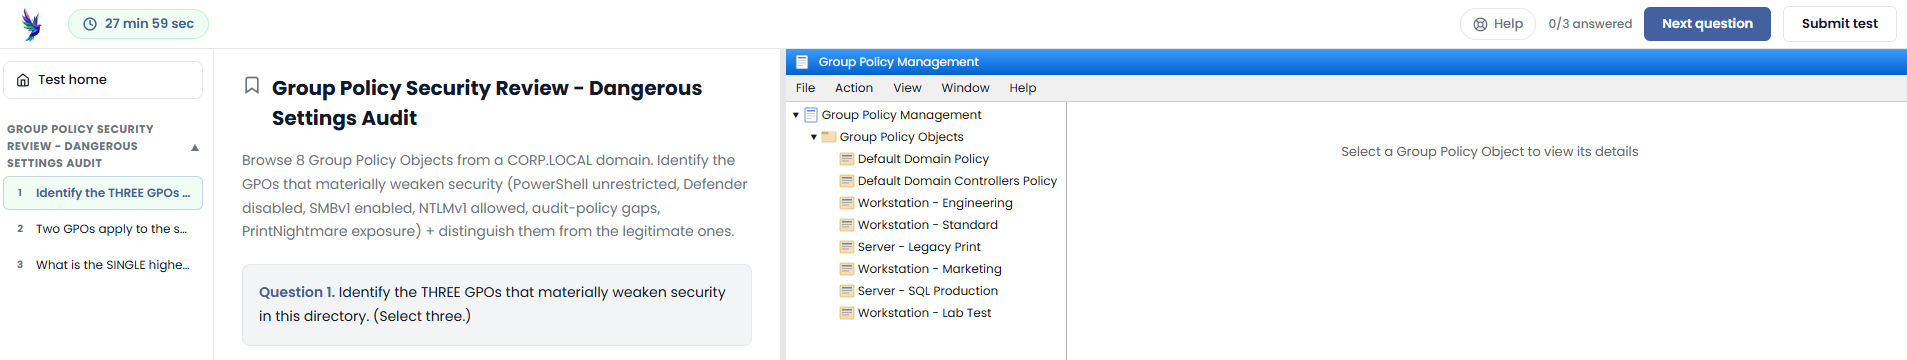
- Group Policy Audit: Insecure Domain Configuration
- Group Policy - Defender Tampering via GPO
Host hardening
- Linux File Permissions & System Hardening
6 challenges · about 116 minutes as listed · trim or swap any of them for your role
One case, end to end
What a strong answer actually looks like.
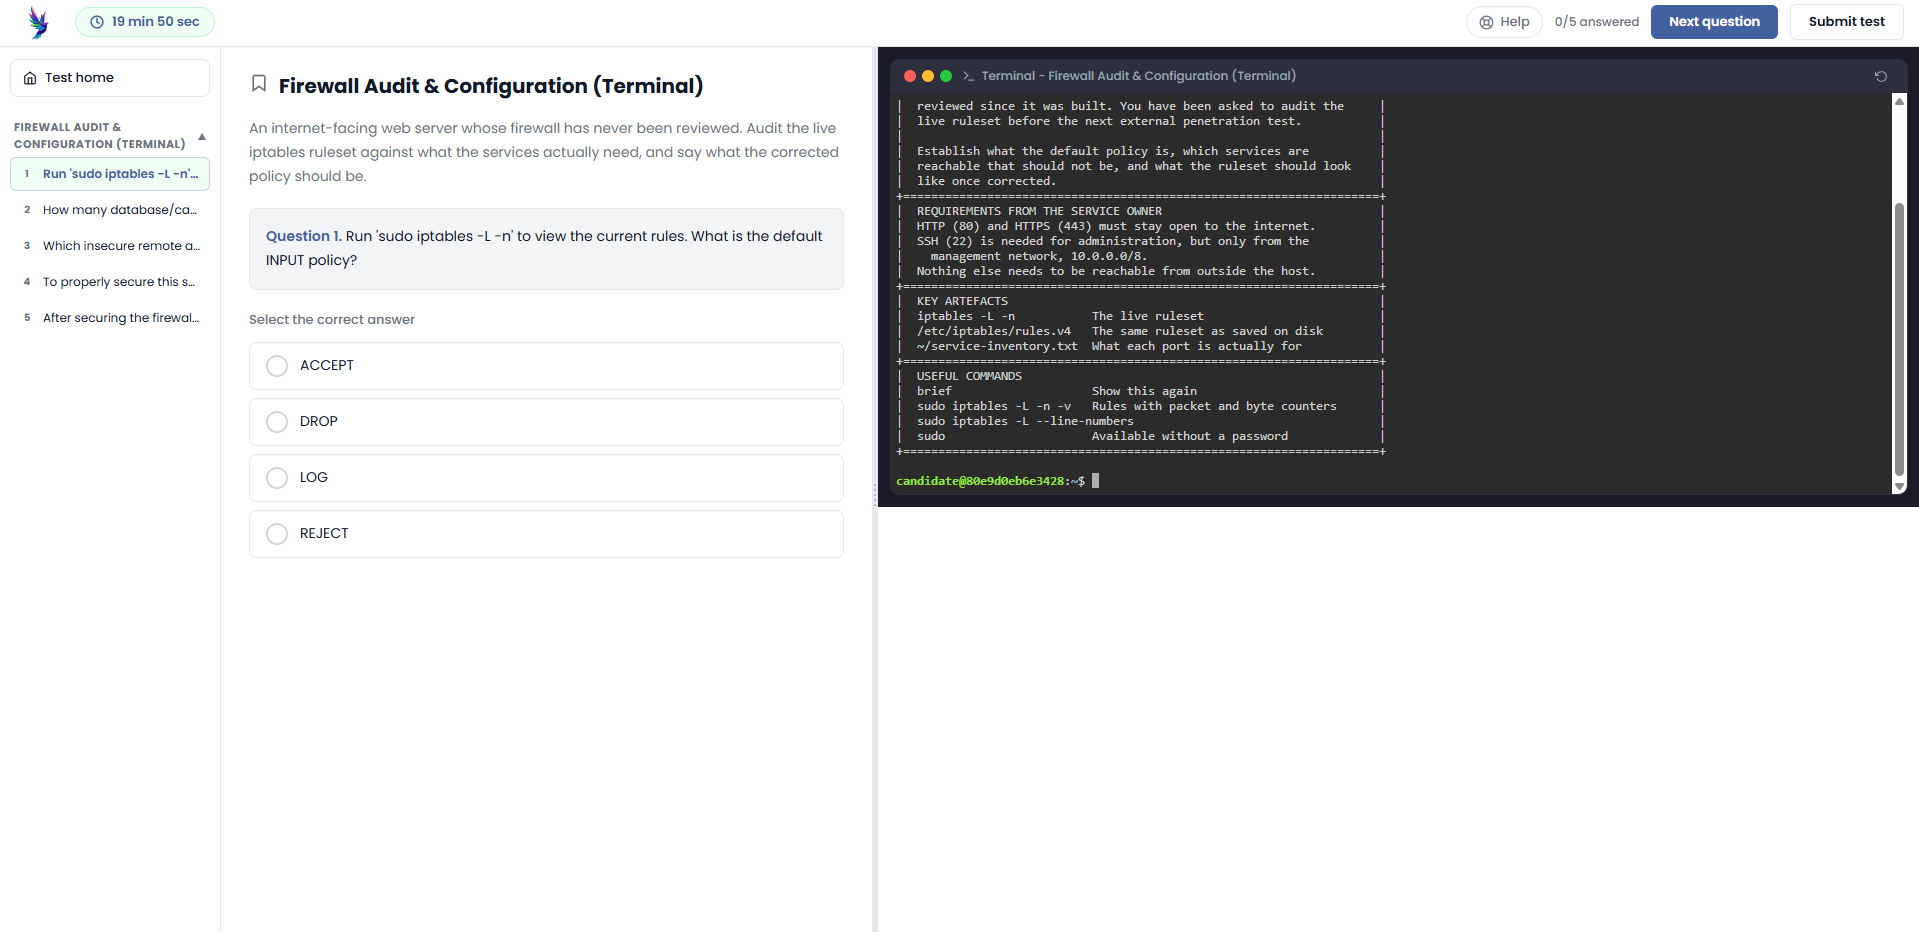
An internet-facing web server whose firewall has never been reviewed. The service owner needs web traffic open to the internet, SSH from the management network only, and nothing else reachable. Audit the live ruleset against that, and say what the corrected policy should be.
Reads the live rules rather than trusting the saved file, works out what the current policy actually lets in, names every exposed service that should not be reachable and why it matters, and proposes a policy that keeps exactly what the service owner asked for and nothing more.
Closes the most obviously dangerous port and moves on, without fixing the policy underneath, so the next service someone starts on that host is exposed as well.
The candidate's screen
Real configuration, with the weak control left in.
Some settings weaken security and some only look like they do. Telling the two apart is the task.
Free, before you commit to anything
See it before a candidate does.
Tell us the role. We build a hands-on security engineer assessment for it, in your branding, and send you a private link to sit it yourself. If it is not right for your team, you have lost nothing.
- 01 Tell us the role Send the job spec or just the role title. A job description helps but is not required.
- 02 We build it for you We turn the spec into a hands-on security engineer assessment from real challenges, at the right level, in your branding.
- 03 Invite your applicants You get a private link to try it first. When you are happy, send it to your applicants. That is it.
What you get back
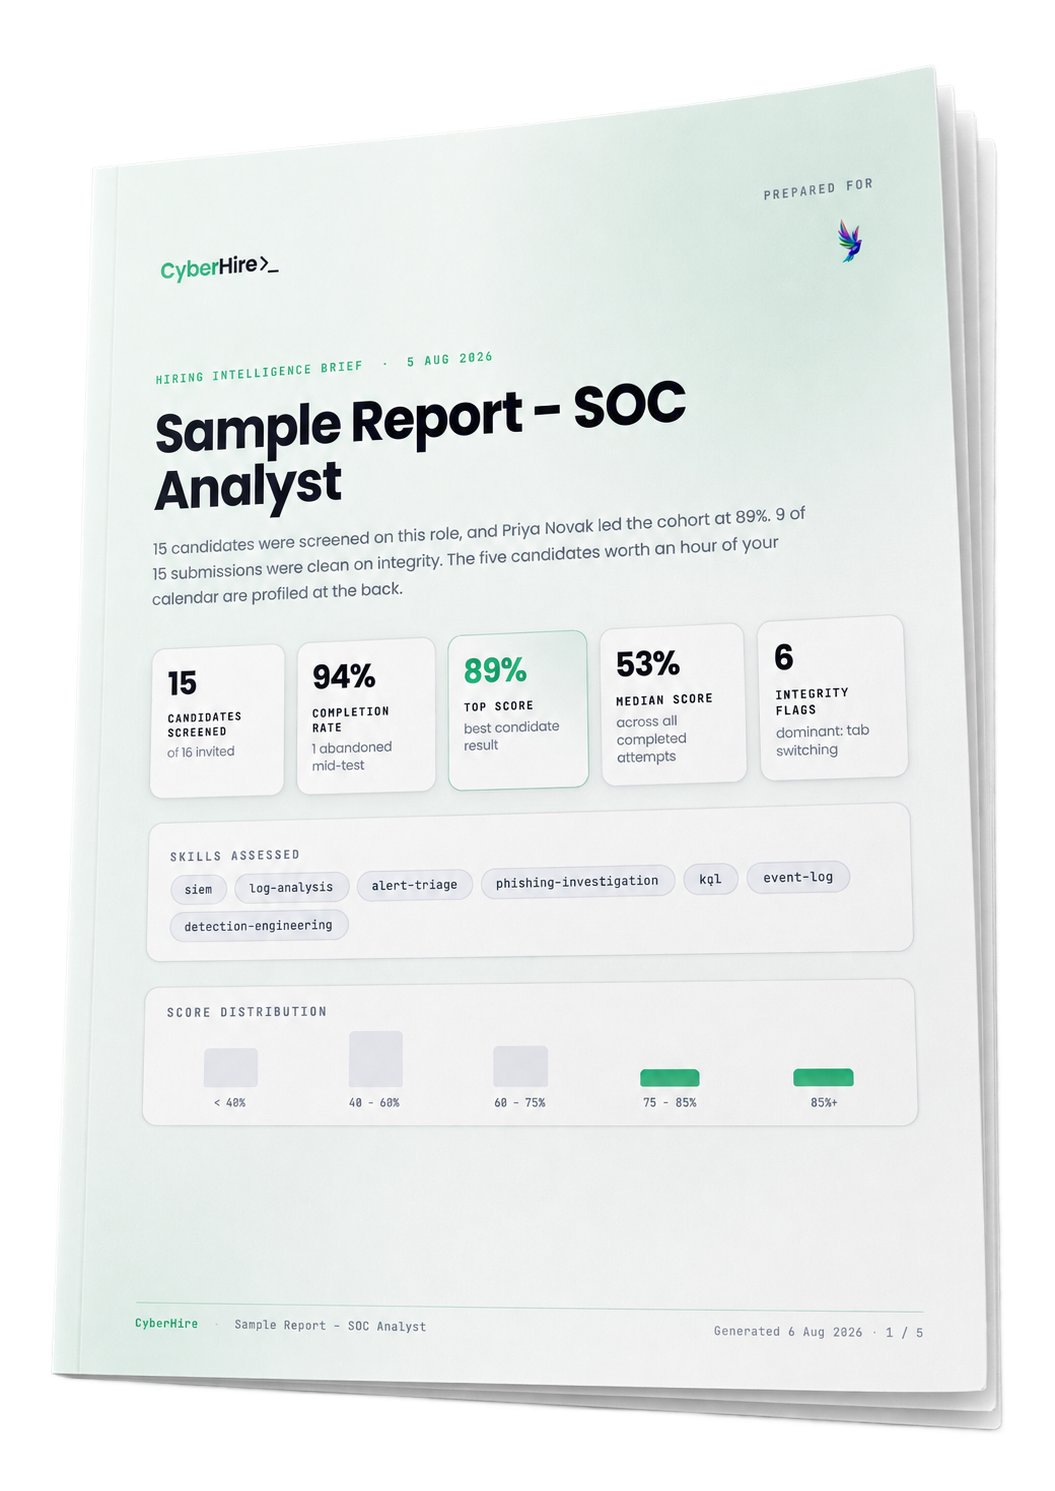
Evidence for every candidate. Read in two minutes.
Results arrive in your workspace as candidates finish, and as a hiring report you can forward to anyone on the panel, including people who never log in. Connected to your ATS, the result is written back to the candidate record.
- Ranked, scored the same way Every candidate on the same challenges and the same answer key, ranked on what they did.
- A score per skill Where each candidate is strong and where they are thin, with their actual answers underneath.
- What to probe at interview For every candidate: the skills they were weakest on and the questions behind it.
- Integrity next to every score Time away, outside pasting, fullscreen exits and second screens, flagged for you to weigh.
How it runs
From job spec to evidence you can act on.
- 01
Send us the role
Fill in the form with the job spec, or just the role title. That is all we need from you.
- 02
We build your assessment
Hands-on, built to your role and level, in your branding, and ready to send. Change anything you like, or send it exactly as it is.
- 03
Invite candidates
A link, a secure bulk upload or straight from your ATS. Everyone sits the same assessment.
- 04
Candidates do the work
In a live shell and real consoles, in your branding, with integrity monitoring on.
- 05
Read the evidence
A ranked cohort, a score per skill, the questions to probe with each candidate and any integrity signals.
Questions we get asked
Security engineer hiring questions, answered.
How do you assess a security engineer before interview?
Give them a piece of the real job: a firewall ruleset to review, a Group Policy configuration to audit, a host to harden or a packet capture to read. Score what they find, then use the interview to explore their reasoning and the trade-offs.
Can the assessment match our environment?
Yes. We build it from your job specification, weighted to the areas the role covers, such as network security, Windows policy or Linux hardening, at the level you are hiring. You can change anything before it goes out.
We use a specific firewall vendor. Does that matter?
The challenges test the reasoning that transfers between products: reading a ruleset against what the services need, spotting segmentation gaps and judging a change. They use Linux iptables and firewall rule sets reviewed as configuration, rather than one vendor's console.
What stops candidates using AI?
The answers sit in the configuration in front of the candidate, so there is little a model can answer from general knowledge. Time away from the test, outside pasting, fullscreen exits and second screens are recorded next to every score.
Do we still need to interview?
Yes. The assessment shows who can do the work and where the gaps are. The final interview then goes on design trade-offs, how they handle change and the areas the assessment flagged.
Go deeper
How we think about assessing engineers
None of it is gated.
Try it on your role
See the security engineer assessment built for your role.
Send us the job spec. We build the assessment around it, in your branding, and you try it yourself first. Free, and with no commitment.