
Skills test for hiring
Incident response test for hiring
A hands-on incident response assessment that shows who makes the right call under pressure. Candidates make real containment decisions, reconstruct intrusions from forensic evidence, review chain of custody and judge post-incident reviews, scored the same way for everyone.
14 hands-on challenges · 15 to 30 minutes each · Built around your job spec
What candidates actually do
The work itself. Not questions about it.
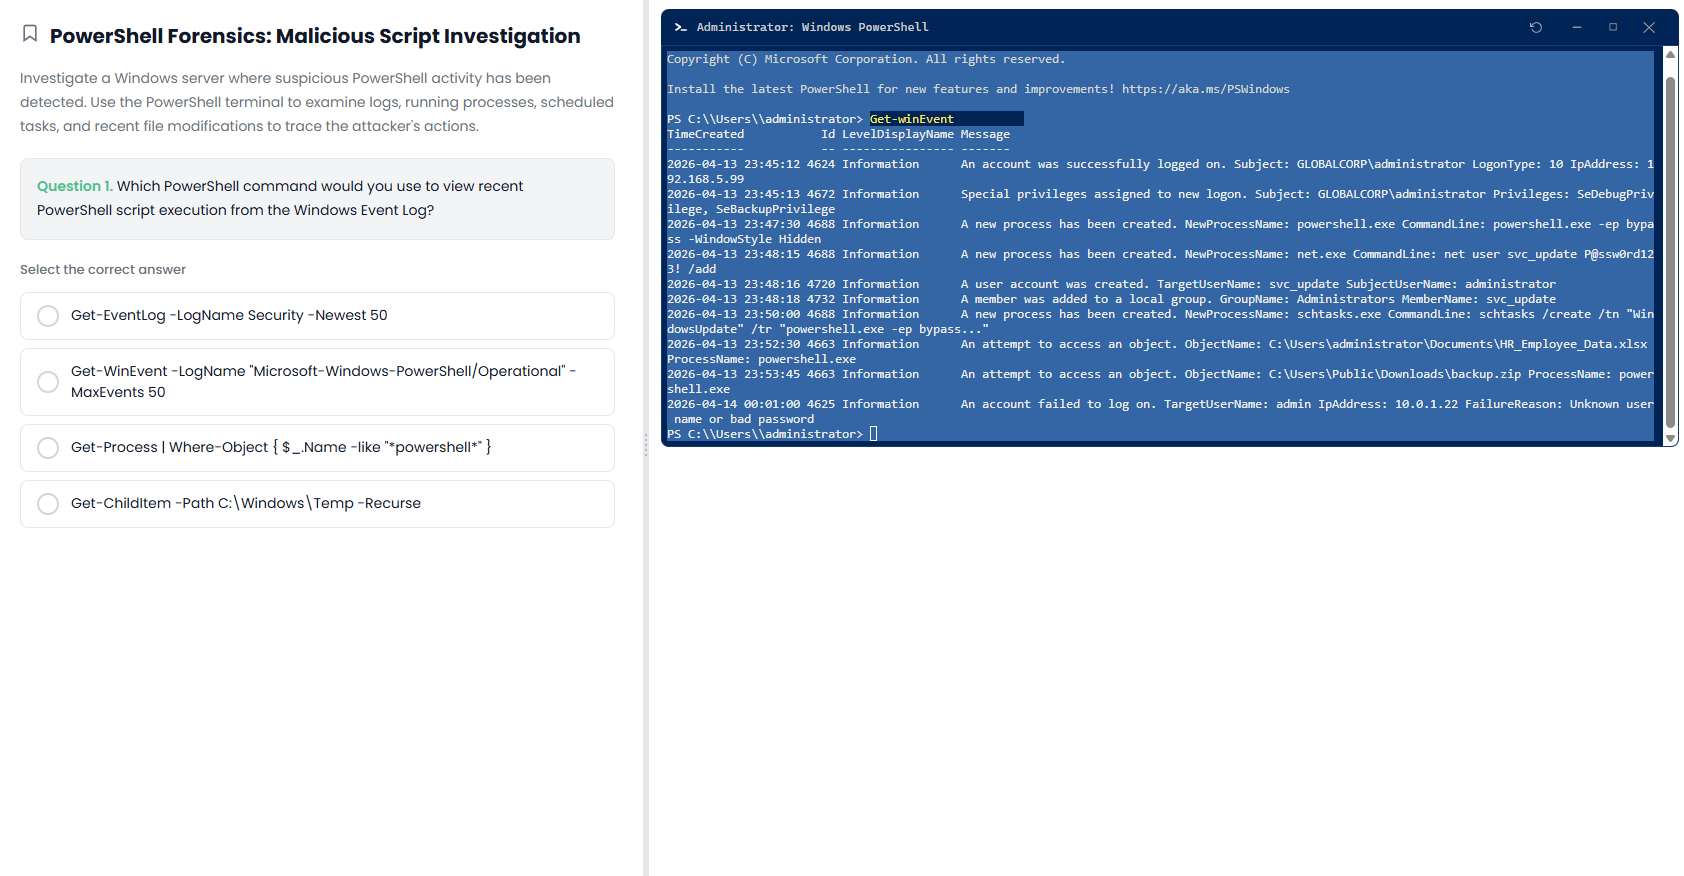
Candidates work in environments that look like the job, on realistic data with legitimate activity left in. The answer only exists in the data in front of them, so there is nothing to look up and nothing to guess between.
- Windows PowerShell
- Registry editor
- Event logs
- Incident documents and evidence
Ransomware: hour-one containment decisions
Machines on the finance network are encrypting and the business wants to know what to do. Choose the first containment actions, in order, and explain the trade-off behind each one.
Isolates affected systems without powering them off, protects and checks the backups, moves communication off possibly compromised email, and brings in leadership, legal and the insurer early, with a reason for each step. A weak answer pulls the plug and loses the evidence.
Skills covered
14 real challenges. Pick the ones that fit the role.
Every assessment is assembled from the library to match your job spec, then calibrated to the level you are hiring. These are the incident response challenges it draws on.
Containment and response decisions
- BEC Response - First 30 Minutes (CFO Wire Request)
- Ransomware - Hour 1 Containment Decisions
- Ransomware Recovery - Restoration Decisions
- Insider Threat - Evidence Handling Decisions
Forensic investigation
- M365 Audit - Auto-Forward Rule + Mailbox Export Investigation
- Registry Forensics - Persistence via Run Keys + Tasks + IFEO
- PowerShell Forensics: Malicious Script Investigation
- Azure AD - AiTM Session Token Theft Investigation
Evidence handling
- Chain of Custody Log - Forensics Evidence Review
Email-borne incidents
- Business Email Compromise Investigation
- Supply Chain Phishing: Vendor Impersonation
Post-incident review
- Incident Lessons-Learned Record - Quality Review
- IR Post-Mortem Review - Phishing to Domain Admin
- Windows Attack-Chain Post-Mortem - Roast to Restore
Levels: 3 Easy · 7 Medium · 4 Hard. Assessments usually combine a few challenges to fit the time you set.
What you get back
Evidence for every candidate. Scored the same way.
Every candidate is scored against the same answers, so you compare the work, not impressions. Read a candidate in two minutes, then interview the ones who can do the job.
- A score per skill See where each candidate is strong and where they are thin, not just a single number.
- Their actual answers Read what they found and how they explained it, so you can probe it in the interview.
- Integrity signals Time away, outside pasting, fullscreen exits and second screens, next to every score.
Roles it fits
Use it for the hire. Then for the interview.
- Incident response interview questions 25 questions with strong answers, grouped by phase.
- How to assess incident response skills The four skills that matter, and what strong and weak attempts look like.
- Incident response hiring with CyberHire How an incident response hiring campaign runs.
- SOC analyst skills test For candidates moving up from the SOC.
Common questions
About the incident response test.
What does the incident response test measure?
Whether a candidate can scope an incident, make sound containment decisions, investigate forensic evidence from PowerShell, the registry and cloud audit logs, handle evidence properly and judge a post-incident review. Each challenge puts real material in front of them.
Can it test decision-making, not just technical skill?
Yes. Several challenges are decision scenarios, such as hour-one ransomware containment, recovery choices and the first 30 minutes of a fraudulent CFO wire request, scored on the decisions and the reasoning behind them.
How long does the incident response test take?
Individual challenges take 15 to 30 minutes. An assessment usually combines a few, matched to the level you are hiring and the time you want to allow.
Who is it for?
Incident responders, senior SOC analysts and anyone who will investigate and contain incidents. Senior and lead roles can focus on decisions and post-incident review; hands-on roles on forensics.
Try it on your role
See the incident response test built for your job spec.
Send us the job spec for a role you are hiring. Within 48 hours we send you a hands-on assessment built around it, in your brand, to try for yourself. Free, and with no commitment.